LIVE INTELLIGENCE FEED / PUBLIC ACCESS

Signal Intelligence

Verified investigations, threat actor unmaskings and open-source intelligence briefings. Every report is reviewed before it enters the feed.

3 ACTIVE REPORTS
3 IDENTITIES UNMASKED
9 TRACKED TAGS
2026-10-12 LAST UPDATE
FILTER:
3 REPORTS IN VIEW
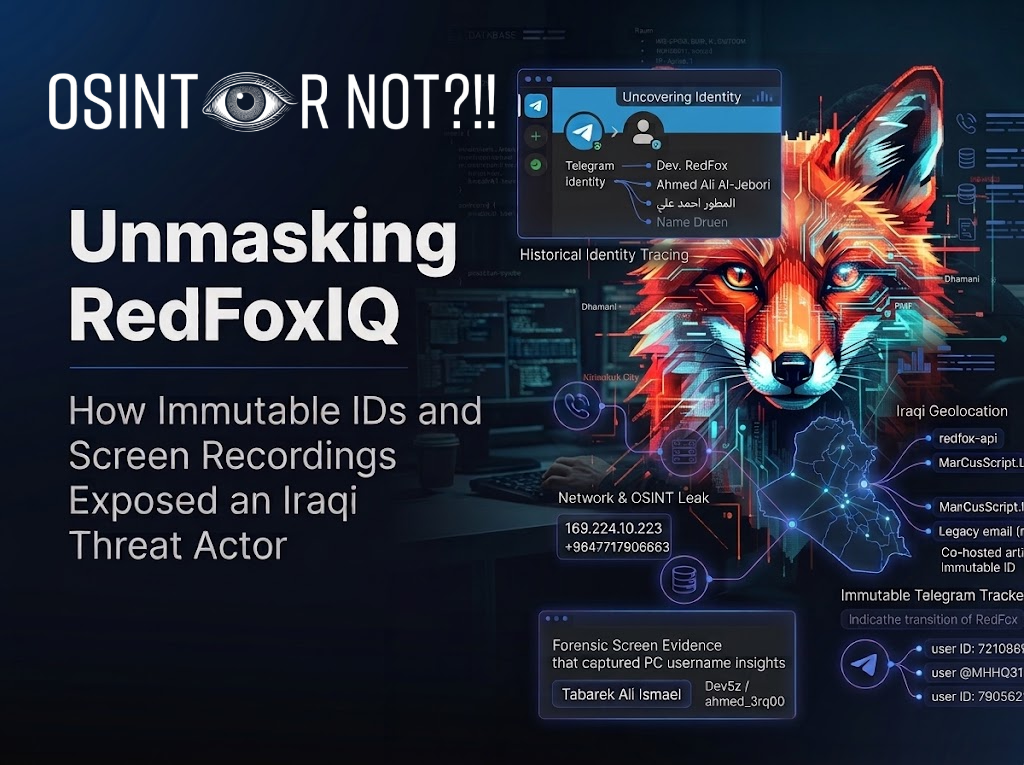
Unmasking RedFoxIQ : How Immutable IDs and Screen Recordings Exposed an Iraqi Threat Actor
2026-09-27 UNMASKED

Unmasking RedFoxIQ : How Immutable IDs and Screen Recordings Exposed an Iraqi Threat Actor

TARGET RedFoxIQ

RedFoxIQ, an Iraqi threat actor responsible for extensive database exfiltrations, was successfully de-anonymized as Ahmed Ali Ismael Al-jebori due to critical operational security failures. Investigators uncovered his true identity by tracking immutable Telegram IDs, reused cross-platform handles, exposed GitHub metadata, and careless screen recordings that revealed his real name and phone number.

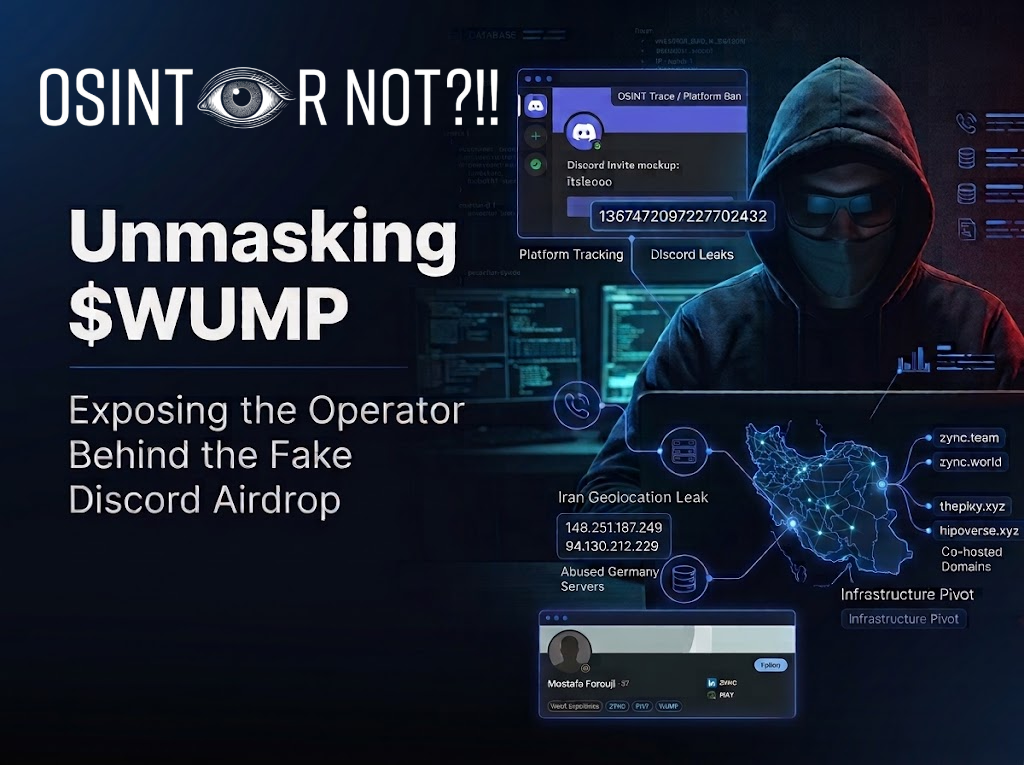
Unmasking $WUMP: Exposing the Operator Behind the Fake Discord Airdrop
2026-09-19 UNMASKED

Unmasking $WUMP: Exposing the Operator Behind the Fake Discord Airdrop

TARGET $WUMP

$WUMP airdrop—masked behind abused German server locations—ultimately unraveled across$HIPO and ZYNC due to leaked Iranian connection telemetry and sloppy infrastructure sharing. These compounding OPSEC failures directly unmasked the operation's sole architect, 37-year-old Iranian operator Mostafa Forouji.

END OF FEED 3 REPORTS INDEXED