
Who Is Anonymous2090?
Anonymous2090 is a financially motivated threat actor and sophisticated data broker who emerged prominently in 2025 and 2026.
Operating as a highly destructive extortion syndicate, the group primarily targets the MENA and GCC regions — specifically Saudi Arabia, the UAE, Egypt, and Yemen — while also successfully compromising high-value global targets, including U.S. classified military infrastructure.
Confirmed Breach Activity
| Publication Date | Target | Country | Sector | Data Compromised |
|---|---|---|---|---|
| September 2, 2025 | Yemen Mobile | Yemen | Telecommunications | Classified corporate infrastructure plans |
| September 20, 2025 | Yemen Net | Yemen | Infrastructure | Complete databases of the ISP |
| September 20, 2025 | US Embassy in Yemen | Yemen / USA | Diplomatic | Classified documents and correspondence (2009-2015) |
| September 20, 2025 | Hodeidah Port | Yemen | Infrastructure | Inbound container reports and shipping data |
| September 29, 2025 | Government & Military Seals | Yemen | Govt / Military | Official seals of ministries, universities, and military |
| February 25, 2026 | Saudi Ministry of Interior | Saudi Arabia | Govt / Security | Complete ministry systems, data and phones of officers |
| March 6, 2026 | Sana’a University | Yemen | Education | University database of academic staff and students |
| March 6, 2026 | Yemen University of Knowledge | Yemen | Education | Student registration database |
| March 13, 2026 | Sana’a Water Corporation | Yemen | Infrastructure | Operational database of the corporation |
| March 13, 2026 | Lebanese Internal Security Forces | Lebanon | Security / Govt | Crime files and classified internal records |
| March 14, 2026 | Mideast.com.sa | Saudi Arabia | Tech / Business | >40 GB (Bank transfers, payment cards, IDs, plates) |
| April 15, 2026 | Jeeny App | Saudi Arabia | Transport | Massive databases (Ride logs, IDs, phone numbers, SMS) |
| April 18, 2026 | Thailand Travel Website | Thailand | Tourism | Tourism database with complete server destruction |
| April 18, 2026 | Lebanese University | Lebanon | Education | Databases of students’ academic and personal records |
| April 21, 2026 | ISIS Terrorist Organization | Global | Terrorism | Organization data and internationally wanted persons lists |
| May 29, 2026 | Naresuan University | Thailand | Education | Academic databases |
| June 2, 2026 | National ID Card Database | Egypt | Government | 2 GB of citizens’ and teachers’ ID card photos |
| June 5, 2026 | Emaar Properties | UAE | Real Estate | Corporate database tables |
| June 9, 2026 | Al Andalus Educational Complex | Qatar | Education | >100 GB (IDs, addresses, photos) with DB destruction |
| June 29, 2026 | Culligan Middle East | UAE | Infra / Water | 28 GB (Databases and source code for all subdomains) |
| July 5, 2026 | Nest Academy Dubai | UAE | Education | Leaked IDs, passports, and academic certificates |
| July 6, 2026 | totalhomecare.ae | UAE | Services | Databases, source code, and WP control panel access |
| July 12, 2026 | US Department of Transportation | USA | Govt / Military | >500 GB (LiDAR data, military maps, drone targeting) |
| July 15, 2026 | Qatar Grand Central | Qatar | Food & Beverage | 44 GB (Sales records, balances, and financial cards) |
| August 8, 2026 | Cleveland Bridge | Saudi Arabia | Contracting | Project blueprints, contracts, ID photos, and source code |
| August 13, 2026 | Qiam Real Estate | Saudi Arabia | Real Estate | 315 GB (Client data, contracts, spreadsheets) |
| September 2, 2026 | SEDER Group | Saudi Arabia | Facilities Mgt | Operational databases, incident reports, and source code |
| September 22, 2026 | Egyptian General Company (EGOTH) | Egypt | Tourism / Hotels | 15 GB (Databases and source code) |
| September 29, 2026 | Financial Regulatory Authority (FRA) | Egypt | Govt / Financial | 12 GB of documents and databases (2022-2026) |
| October 3, 2026 | Sameerali Website | UAE | Transport | >2 GB with persistent backdoors planted in servers |
| October 10, 2026 | Emirates Motorsports Org (EMSO) | UAE | Sports / Org | 95 GB (Passports, national IDs, driver’s licenses) |
| October 10, 2026 | U.S.-Oman Business Council | Oman | Trade / Org | Database backups from 2018 to 2025 |
The DarkForums Breach & IP Exposure
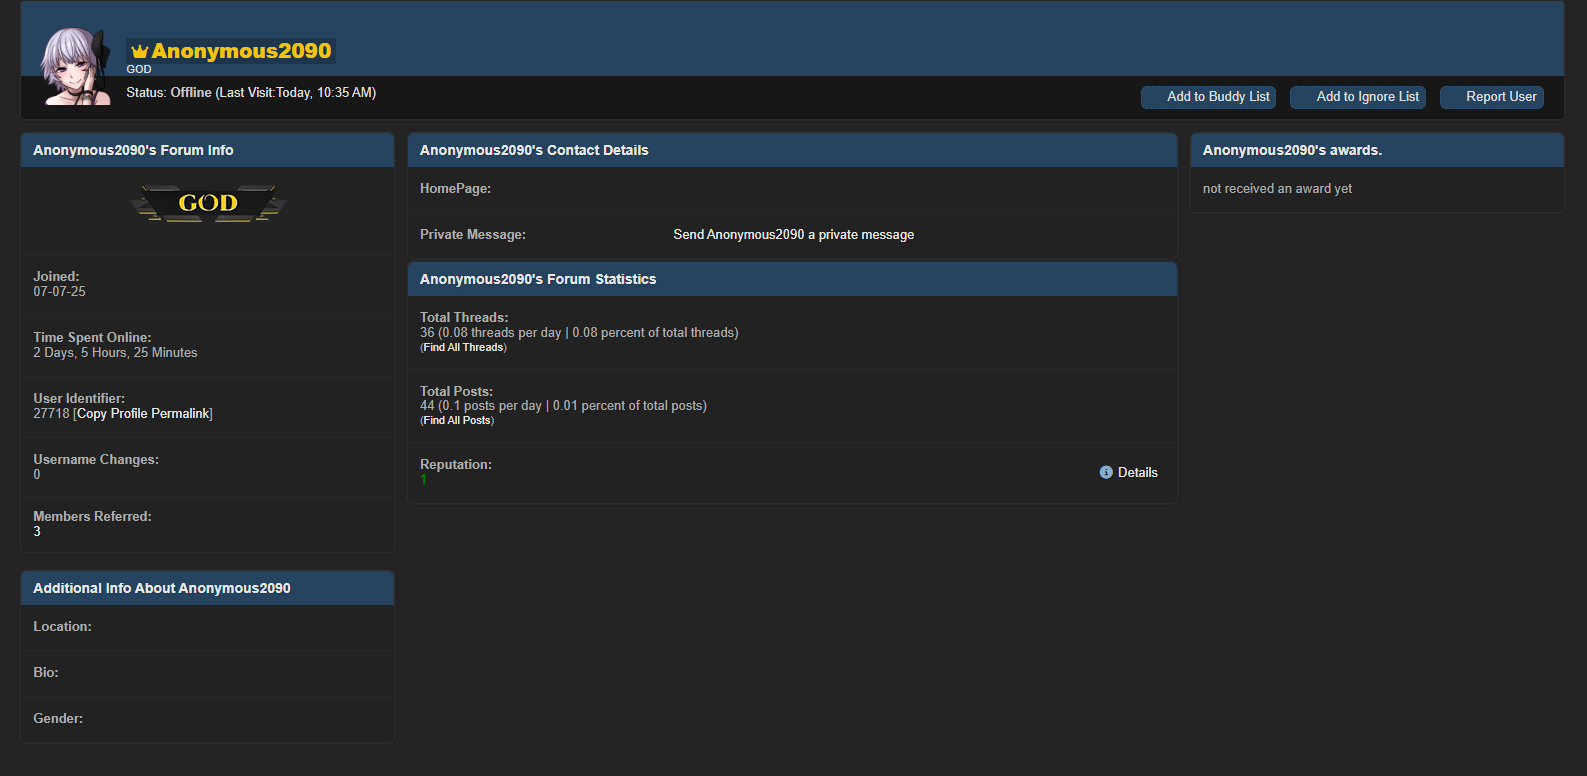
Initiating our OSINT investigation into the actor’s primary alias, we pivoted through historical data breaches, specifically analyzing compromised logs from darkforums.as. While parsing the connection logs associated with their username, we identified a distinct cluster of IP addresses.
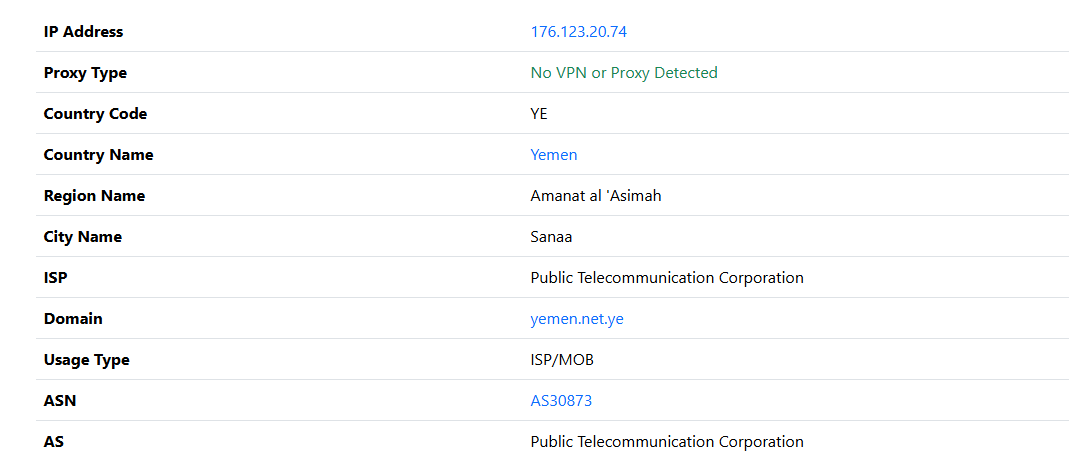
Although Anonymous2090 heavily relies on proxy networks and VPNs to obfuscate their digital footprint, a critical OPSEC oversight resulted in the accidental leakage of several direct, unmasked IP addresses. Geolocation and ASN analysis of these specific, unprotected pings definitively trace the threat actor’s true physical location to Sana’a, Yemen.
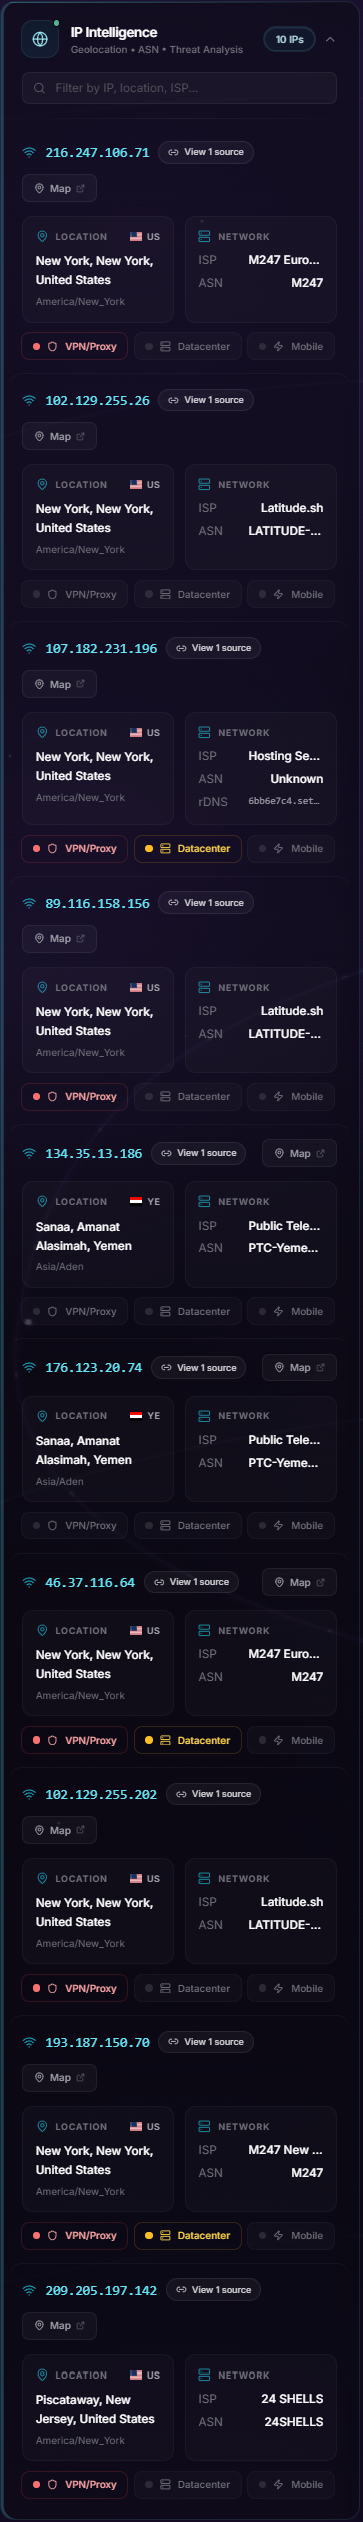
Upon isolating the connection logs tied to the actor’s profile, our investigation extracted two specific, unmasked IP addresses:
134.35.13.186176.123.20.74
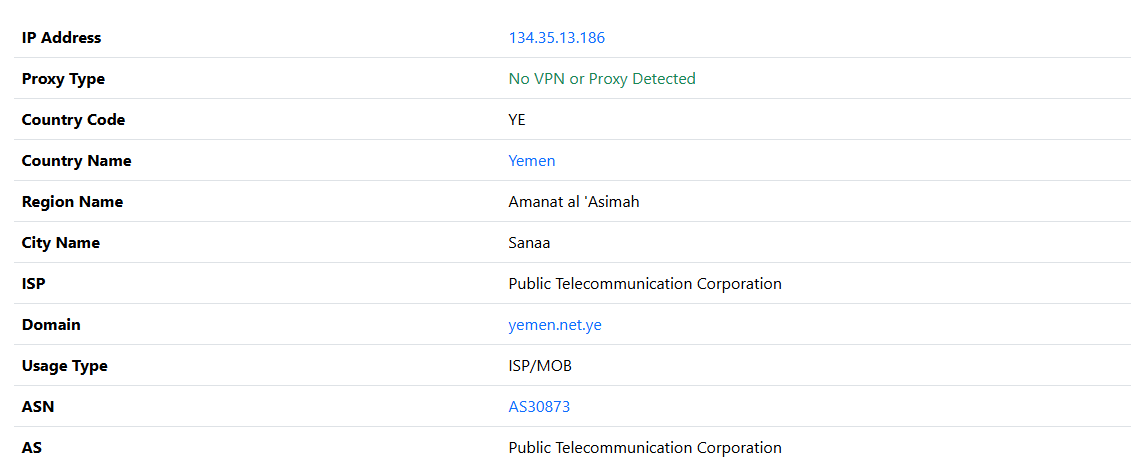
Subsequent technical analysis and IP intelligence enrichment confirmed that these addresses were not routed through Tor exit nodes, VPN providers, or commercial proxy networks. Instead, they are raw, direct connections allocated to local Yemeni Internet Service Providers (ISPs). This critical OPSEC failure bypassed their usual obfuscation layers, firmly anchoring the threat actor’s physical infrastructure and daily operational origin to Sana’a, Yemen.
Telegram Footprint & Behavioral Attribution
Expanding our investigation into the actor’s communication infrastructure, we conducted historical telemetry and channel scraping on their two primary Telegram handles. This analysis provided critical insights into the actor’s background and cultural identity.
Tracing the fulfillment handle, @LockBit_2090, revealed the actor’s past membership in a highly localized, Arabic-speaking Telegram group named “مركز IT net لمستلزمات الشبكات” (IT Net Center for Networking Supplies). This artifact suggests a foundational background or local commercial interest in IT networking and hardware.
Parallel analysis of the primary negotiation alias, @hacker1oo, uncovered their active presence in a specialized, Yemen-based cybersecurity channel titled “𝘼𝙧𝙖𝙗 𝘾𝙮𝙗𝙚𝙧𝙨𝙚𝙘𝙪𝙧𝙞𝙩𝙮 ㉿”.
These behavioral artifacts dismantle the persona of a global, faceless syndicate. The actor’s engagement in local networking commerce groups and regional hacking communities provides conclusive cultural and linguistic attribution. Furthermore, this directly corroborates our earlier IP geolocation, confirming that the threat actor behind Anonymous2090 is a native Arabic speaker operating out of Yemen, with deep roots in the local IT and cybersecurity underground.
PII Extraction & Real-World Identity
To further unmask the operator behind the @LockBit_2090 handle, we queried historical Telegram data leaks and breach repositories. This pivot yielded a critical piece of personally identifiable information (PII): a leaked mobile phone number linked directly to the account.
The exposed number, +967 773 289 860, utilizes the +967 country code for Yemen. This finding is the smoking gun that definitively bridges the actor’s digital persona with a physical telecom subscriber, cementing the geographic attribution and proving beyond doubt that the operator is based in Yemen.
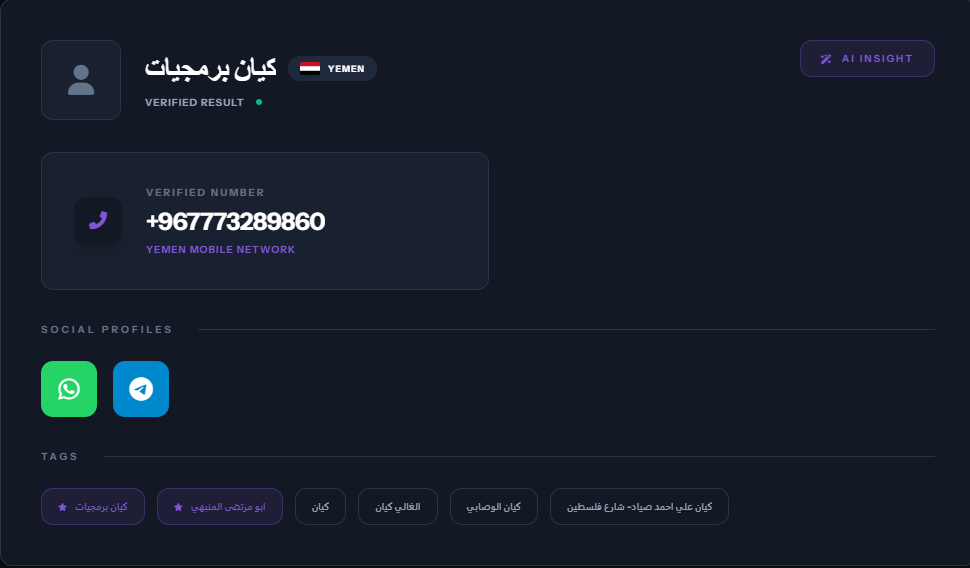
Exploiting this compromised number through various reverse-search methodologies and OSINT tools yielded a distinct cluster of associated names and caller ID tags:
- المبرمج و المهكر كيان (Programmer and Hacker Kian)
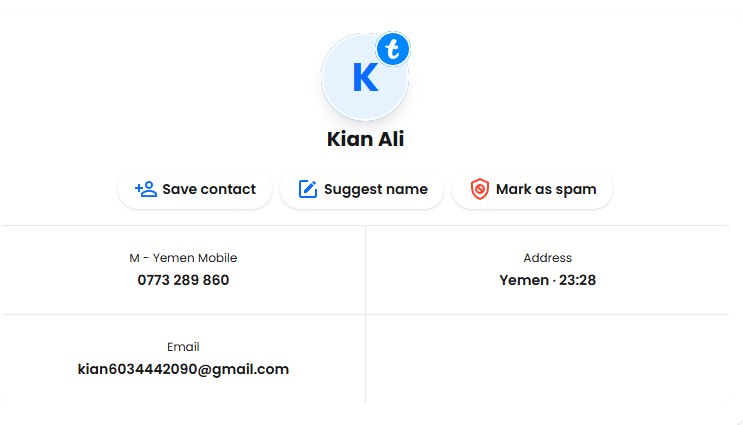
- Kian Ali
- كيان للبرمجيات (Kian for Software)
- ابو مرتضى المنبهي (Abu Murtada Al-Munabbi)
- كيان علي احمد صياد - شارع فلسطين (Kian Ali Ahmed Sayyad - Palestine Street)
- كيان الوصابي (Kian Al-Wasabi)
- الغالي كيان (Dear Kian)
- كيان (Kian)
These overlapping data points consistently isolate “Kian” as the threat actor’s real name. Furthermore, the discovery of a full name (Kian Ali Ahmed Sayyad) coupled with a specific physical location tag (Palestine Street) transitions the profile from a digital pseudonym to a concrete, real-world identity.
Digital Footprint & Real-World Anchoring
Building upon this identity resolution, our investigation successfully extracted the threat actor’s primary email address: [email protected]. This discovery solidifies the attribution—the prefix “Kian” aligns perfectly with our reverse phone lookup results, while the “2090” suffix directly correlates with the “Anonymous2090” alias used across dark web forums, definitively linking the real-world individual to the cybercriminal persona.
Geolocation via Google Reviews
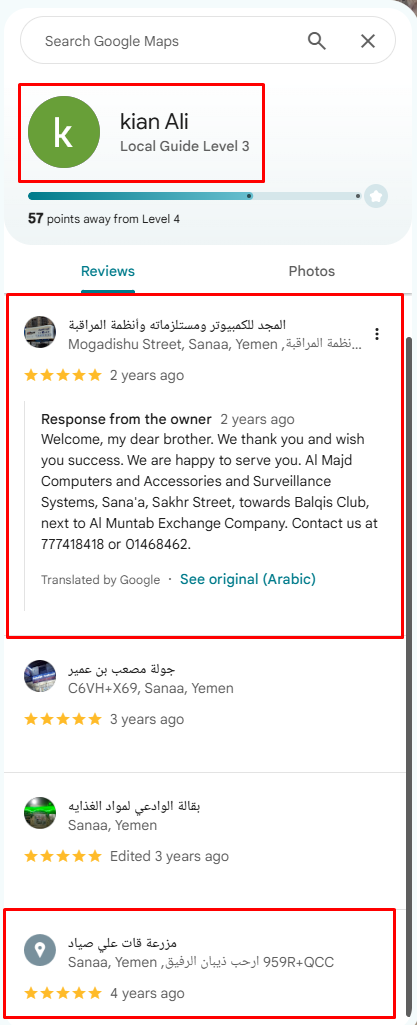
Pivoting off the discovered email address, we conducted a comprehensive trace of its associated digital footprint across public platforms. This investigation uncovered Google Reviews left by the actor, providing further behavioral and geographical context.
The actor left specific reviews for two local establishments:
- “المجد للكمبيوتر ومستلزماته وأنظمة المراقبة” (Al-Majd for Computers, Accessories, and Surveillance Systems): This review reinforces the actor’s previously established connection to the local IT hardware and networking sector in Yemen.
- “مزرعة قات علي صياد” (Ali Sayyad Khat Farm): This is a critical finding. The name of the farm (“Ali Sayyad”) directly corresponds to the patronymic portion of the actor’s identified real name (Kian Ali Ahmed Sayyad). This strongly suggests a familial connection to the location, transforming a simple review into a concrete, real-world geographical anchor linked directly to the threat actor’s family.
Alias Continuity: poq2090 and kian2090
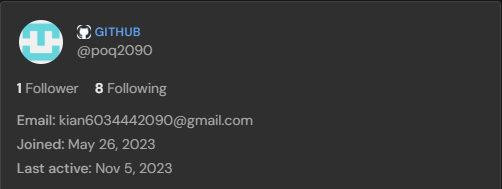
Further enumeration of the email address revealed additional registered accounts across public platforms with activity logs tracing back to 2023:
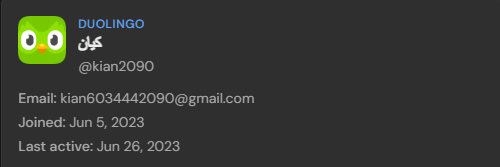
- An account on Duolingo under the username
kian2090. - An account on GitHub, a platform dedicated to developers, under the username
poq2090.
These findings provide valuable insight into the actor’s earlier digital footprint, demonstrating their consistent use of the “2090” numeric suffix and their real name well before the emergence of the Anonymous2090 extortion persona in 2025.
Threat Evolution: From Cracked Tools to Initial Access
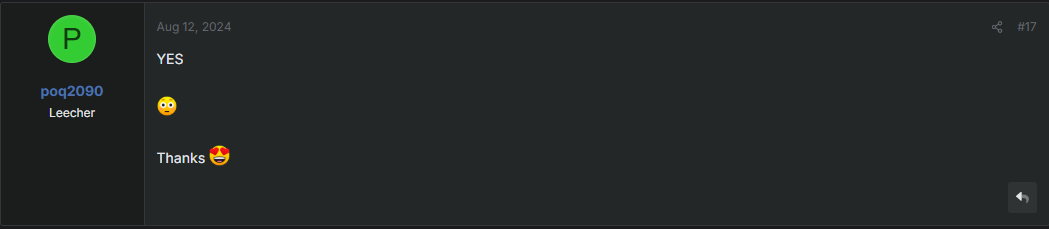
Pivoting off the discovered GitHub username @poq2090, our investigation traced the actor’s footprint to a forum thread discussing cracked tools, where the user had actively posted a reply.
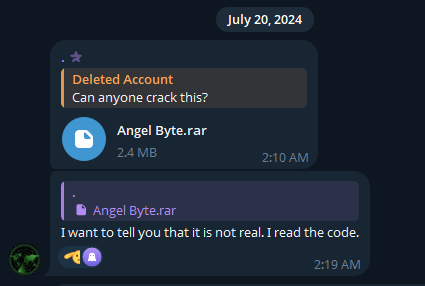
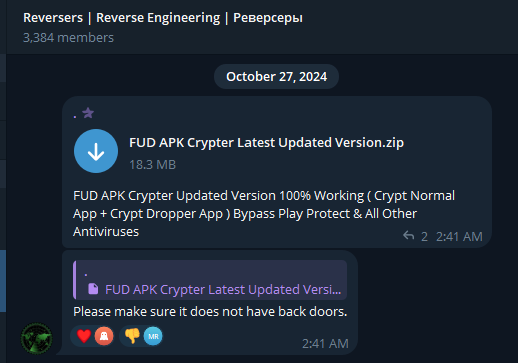
Further analysis of this alias revealed a deep, early interest in software cracking and reverse engineering. Specifically, the actor was identified as an active participant in a Telegram channel named “Reversers | Reverse Engineering | Реверсеры”.
On July 20, 2024, the actor demonstrated a strong passion for software piracy by actively sharing cracked tools within this community, with subsequent distribution activity recorded on October 27, 2024. This behavioral pattern and consistent alias usage definitively confirm that the individual distributing cracked software under @poq2090 is the same threat actor operating as Anonymous2090. It also highlights their technical trajectory—evolving from a consumer and distributor of cracked tools in mid-2024 to a highly destructive data broker breaching sovereign infrastructure by 2025.
BreachForums & Cybercrime Escalation
Deepening the investigation into the @poq2090 alias yielded two additional critical findings that map the actor’s escalation into underground cybercrime:
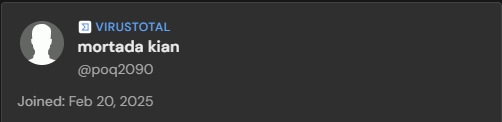
- VirusTotal Profile: An account registered under the same username, displaying the profile name “mortada kian”. This is a crucial attribution link: it combines his own name (Kian) with the name of his son (Mortada), which perfectly aligns with the previously discovered real-world alias “ابو مرتضى المنبهي” (Abu Murtada — Father of Mortada). This explicitly ties his malware-scanning and analysis activity back to his verified family identity.
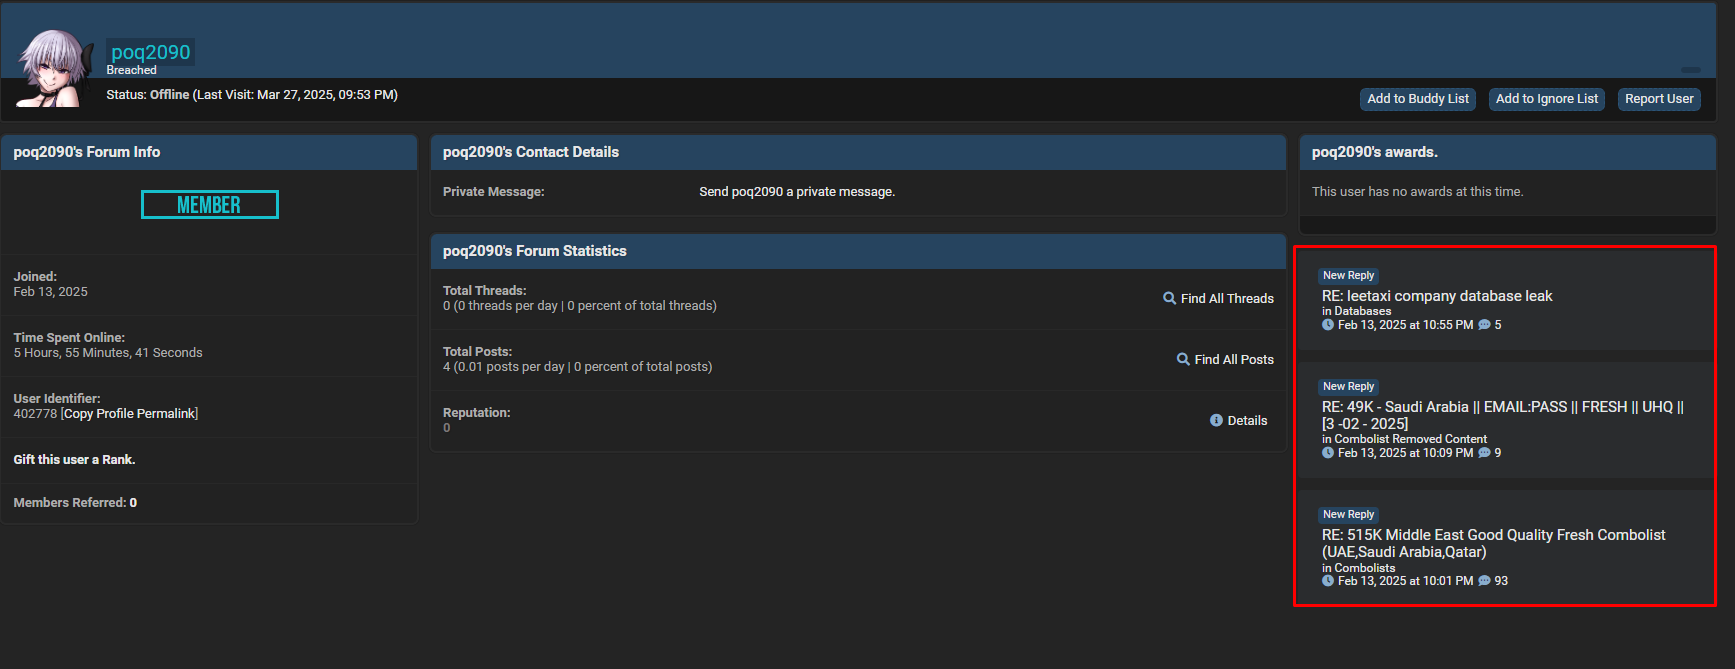
- BreachForums Activity: An active profile on the cybercrime platform utilizing the
poq2090handle. Activity logs reveal the actor explicitly searching for and requesting “ulp logs” (Universal Logs Parser / info-stealer logs).
The pursuit of stealer logs on underground forums represents a pivotal shift in the actor’s threat profile. It demonstrates a deliberate transition from reverse-engineering cracked software to actively hunting for compromised corporate and government credentials—the exact initial access vectors typically utilized to breach the sovereign networks he later compromised and destroyed as Anonymous2090.
Infrastructure Overlap & Collateral Associates
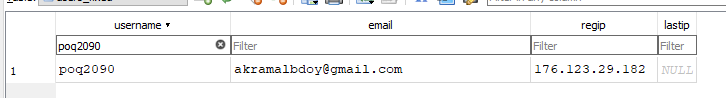
Cross-referencing the @poq2090 username against historical BreachForums database leaks uncovered additional operational security failures. The compromised forum records exposed a secondary, previously unknown email address linked to the profile: [email protected].
Crucially, the database leak also captured the account’s historical registration and login IP address: 176.123.29.182. This specific IP address falls within the exact same Yemeni ASN and /16 subnet (176.123.x.x) as the direct, unmasked IP address (176.123.20.74) previously identified in the darkforums.as logs. This subnet overlap definitively corroborates the actor’s physical location in Sana’a, Yemen, and provides absolute technical confirmation that the poq2090 BreachForums identity and the Anonymous2090 extortion persona are operated by the exact same individual from the same local infrastructure.
Extensive pivoting and OSINT analysis on this newly discovered email address ([email protected]) yielded a complete lack of associated public records, social media profiles, or secondary accounts. This zero-footprint status strongly indicates that it was a purpose-built burner or “alt” email, deliberately employed to compartmentalize illicit forum activities and evade direct attribution back to the primary “Kian” identity.
Infostealer Collateral
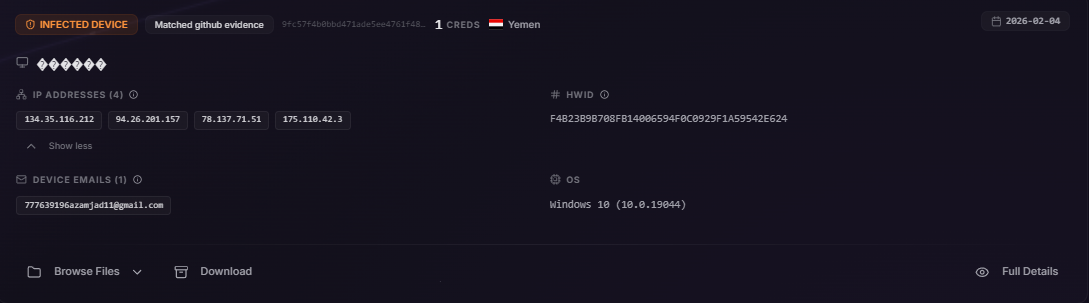
Further analysis of underground infostealer markets revealed a compromised device located in Yemen that contained login autofill data specifically using the poq2090 username. Interestingly, the email address tied to this compromised environment was [email protected].
Network telemetry extracted from this infostealer log exposed a cluster of connection IPs originating from Sana’a: 134.35.116.212, 94.26.201.157, 78.137.71.51, and 175.110.42.3.
The intersection of the highly specific poq2090 alias with a distinct email address, all operating within the same localized Yemeni infrastructure, strongly suggests a shared physical or network environment. This indicates that the individual behind this secondary email is a close associate, relative, or collaborator of the primary threat actor (Kian), potentially sharing devices or operating in tandem from the same base in Sana’a.
Investigation Methodology & Key OSINT Takeaways
- Infrastructure Logging & Subnet Correlation: The foundation of this attribution relied on identifying unmasked telemetry within compromised forum logs. By extracting raw, direct ISP connections (
134.35.13.186,176.123.20.74) fromdarkforums.asand cross-referencing them against historical BreachForums registration IPs (176.123.29.182), the investigation successfully mapped a consistent/16Yemeni subnet. This proved that despite the actor’s use of proxies, the underlying infrastructure consistently originated from Sana’a. - Data Breach Pivoting for PII Extraction: The critical breakthrough in moving from a digital pseudonym to a physical identity was achieved by querying historical Telegram database leaks. Extracting the
+967 773 289 860mobile number linked to the@LockBit_2090handle provided the exact pivot point needed to perform reverse caller-ID lookups, ultimately exposing the actor’s real name (Kian Ali Ahmed Sayyad) and local aliases (Abu Murtada). - Behavioral & Geographic Anchoring: The investigation utilized open-source behavioral artifacts to anchor the threat actor to a concrete physical reality. By tracing the
[email protected]email to specific Google Reviews (Ali Sayyad Khat Farm and a local IT hardware store), the analysis transformed digital footprints into real-world geographic coordinates and familial ties, entirely dismantling the illusion of a faceless, global syndicate. - Alias Continuity and Threat Evolution Tracking: Tracking the persistent use of the “2090” numeric suffix enabled the correlation of disparate accounts across platforms (Duolingo, GitHub, VirusTotal). This longitudinal tracking exposed the actor’s technical evolution over time—mapping the exact trajectory from distributing cracked software in Telegram reverse-engineering channels to actively hunting for Universal Logs Parser (ULP) data on underground forums.
- Exploiting the Actor’s Own Attack Vectors: In a critical reversal of tactics, the investigation utilized the very infostealer ecosystems the actor relied upon to map their local network. By analyzing compromised device logs that captured the
poq2090autofill data alongside an associate’s email ([email protected]) and local Sana’a IPs, the investigation successfully mapped the actor’s collateral environment and potential operational allies.
The unmasking of Anonymous2090 demonstrates the effectiveness of chained, multi-disciplinary OSINT methodologies. By aggressively pivoting between passive DNS analysis, historical data breaches, social media enumeration, and behavioral profiling, independent intelligence efforts can successfully penetrate the operational security of highly destructive threat actors. This case illustrates that no matter how sophisticated the extortion operation appears, consistent OPSEC failures—ranging from burner email mismanagement to localized forum participation—will inevitably leave a traceable, definitive path directly to the operator.