
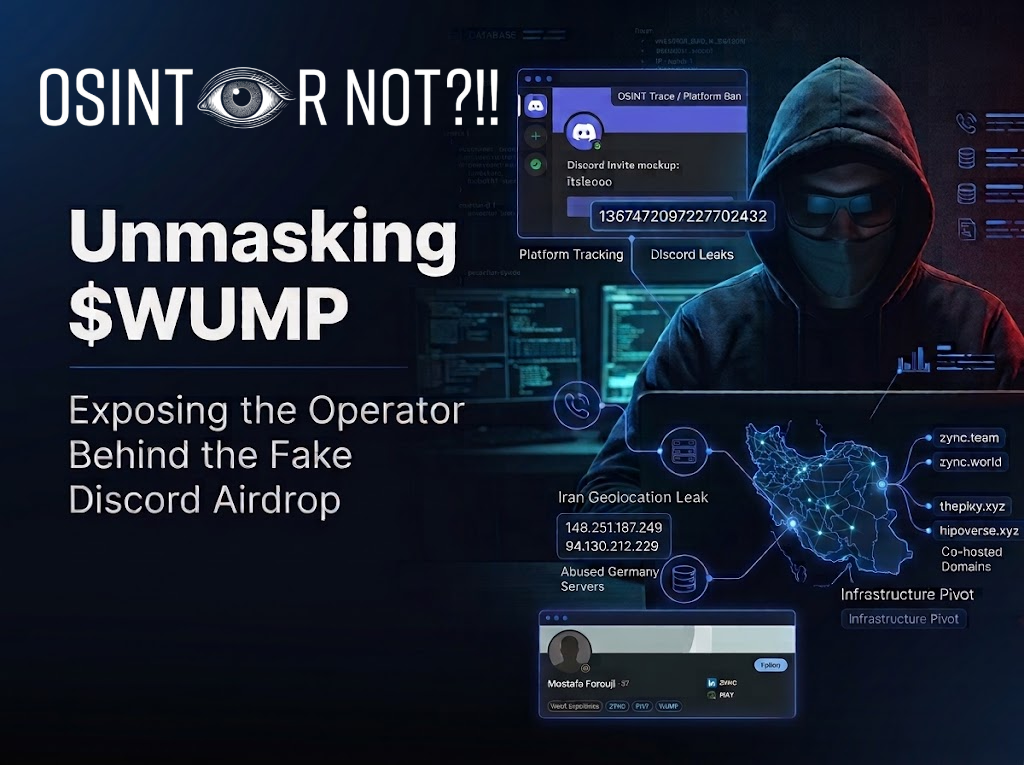
What Is $WUMP ?
The $WUMP campaign was an elaborate, mass-scale social engineering and data harvesting operation. By redirecting targets through a legitimate Discord OAuth2 login flow, the operator bypassed traditional suspicions surrounding wallet-drainers. Instead of attempting immediate financial theft, the malicious application requested excessive read permissions. Through this mechanism, it scraped verified email addresses, joined servers, and critical guild membership roles from over half a million users. The resulting database functioned as a highly curated target list, specifically profiling server administrators and Web3 community moderators for devastating downstream phishing and account takeover attacks.
Who Is Behind The $WUMP?
Behind the veneer of an ambitious Web3 initiative stood a single orchestrator operating behind carefully curated aliases. While the project presented itself as a collaborative venture with a dedicated legal and development team, digital artifacts tell a much different story. The operation relied on a centralized administrative footprint, where minor operational security (OPSEC) failures in infrastructure deployment and social media footprinting left a clear investigative trail.
Initial Footprint & The Fake Airdrop Launch
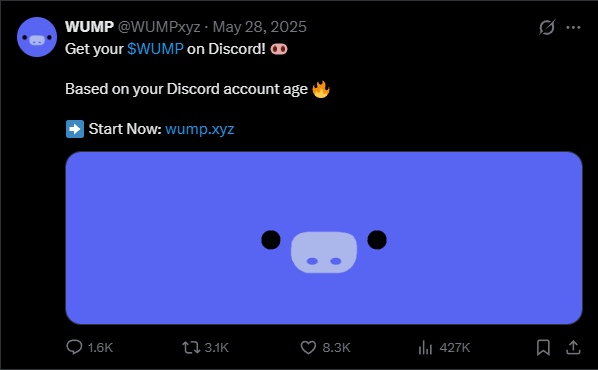
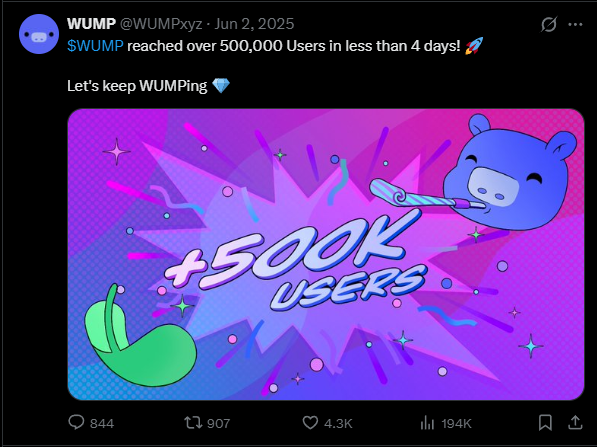
On May 28, 2025, an account named @WUMPxyz surfaced on X (formerly Twitter) to announce a fake Discord-affiliated cryptocurrency, promising users rewards scaled directly to their Discord account’s age.
Geolocation Contradiction: Germany vs. Iran
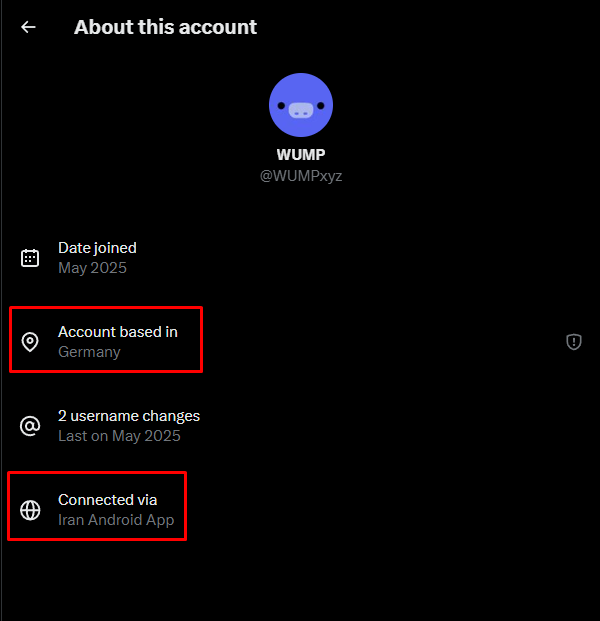
Upon reviewing the “About” section of the @WUMPxyz profile, conflicting geolocation indicators surfaced immediately. While the account location was listed in Germany, its client connection telemetry showed access routed via an Android app in Iran.
The Dead Discord Invite
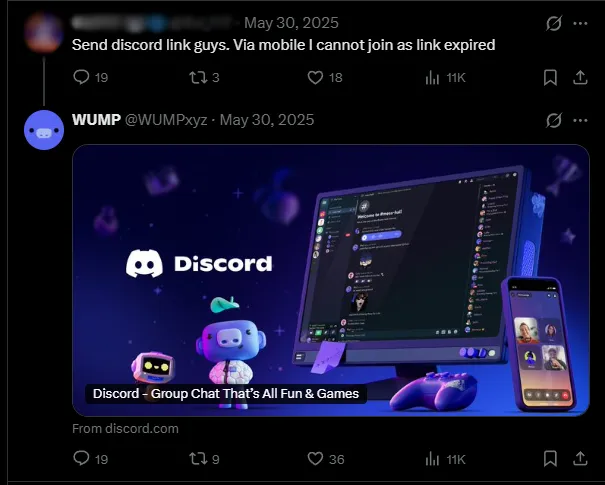
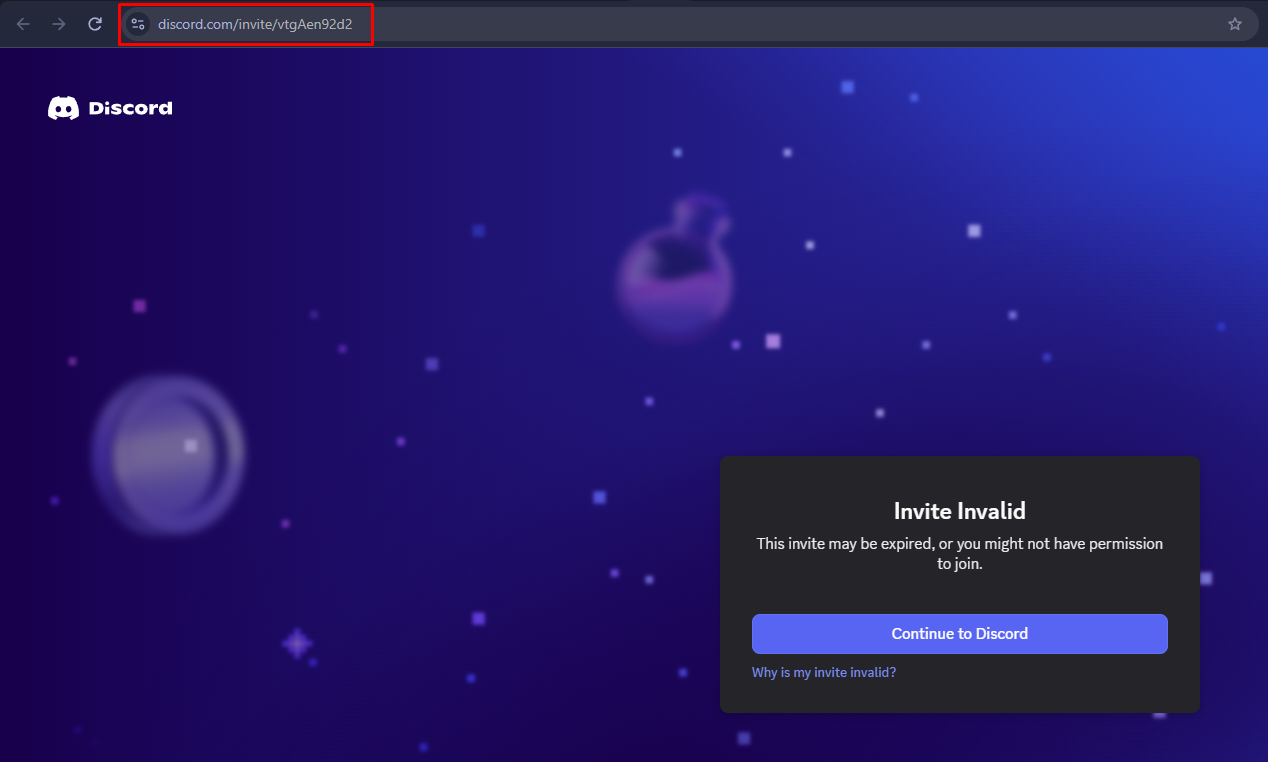
While reviewing the account’s replies, we identified a Discord invite link posted by the cyber criminal; however, the link was already invalid and no longer functional.
WayBack Machine Retrieval: Uncovering Ephemeral Artifacts
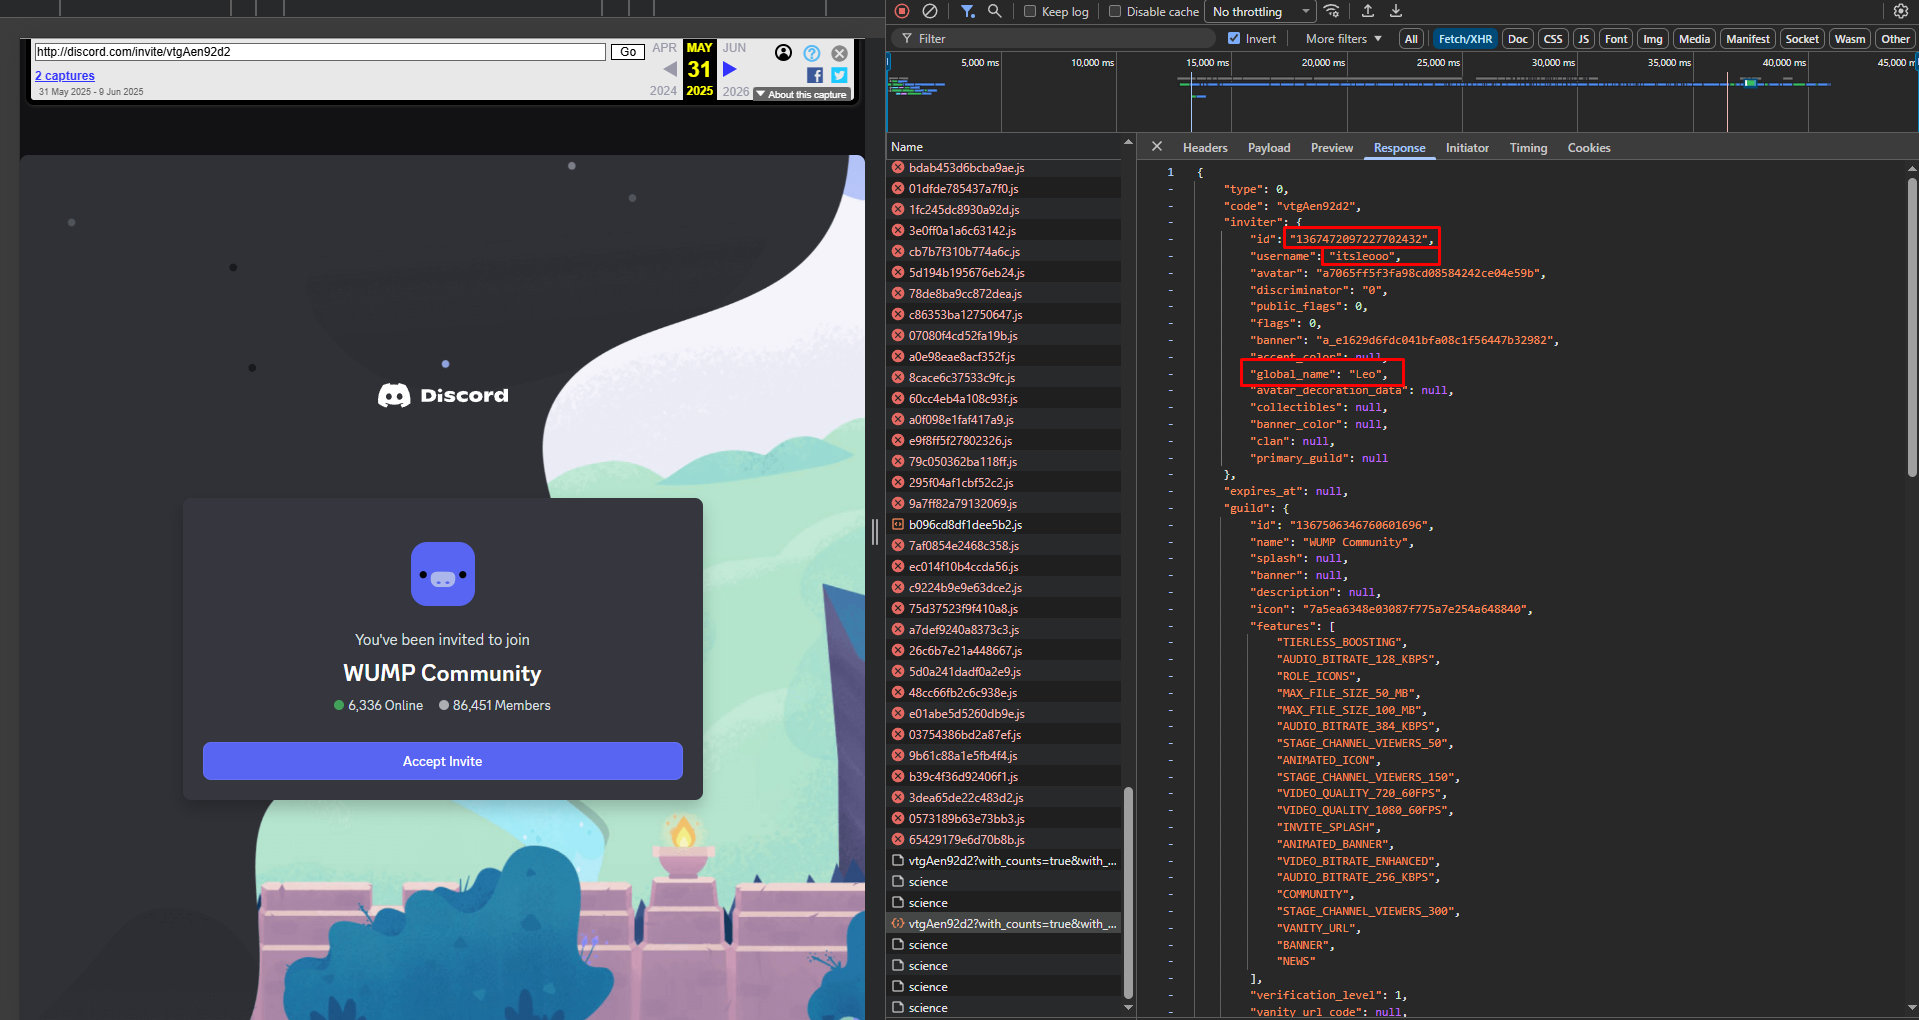
However, the Web Archive never forgets what has once been seen.
Unmasking the Operator’s Discord Persona (itsleooo)
Inspecting the archived API response revealed the underlying profile behind the server invite. Most notably, the payload exposed the cyber criminal’s unique User ID (1367472097227702432), along with the handle itsleooo and display name Leo, providing a permanent pivot point for attribution regardless of subsequent profile modifications.
Discord Platform Ban: Exposing the Fraud Enforcement
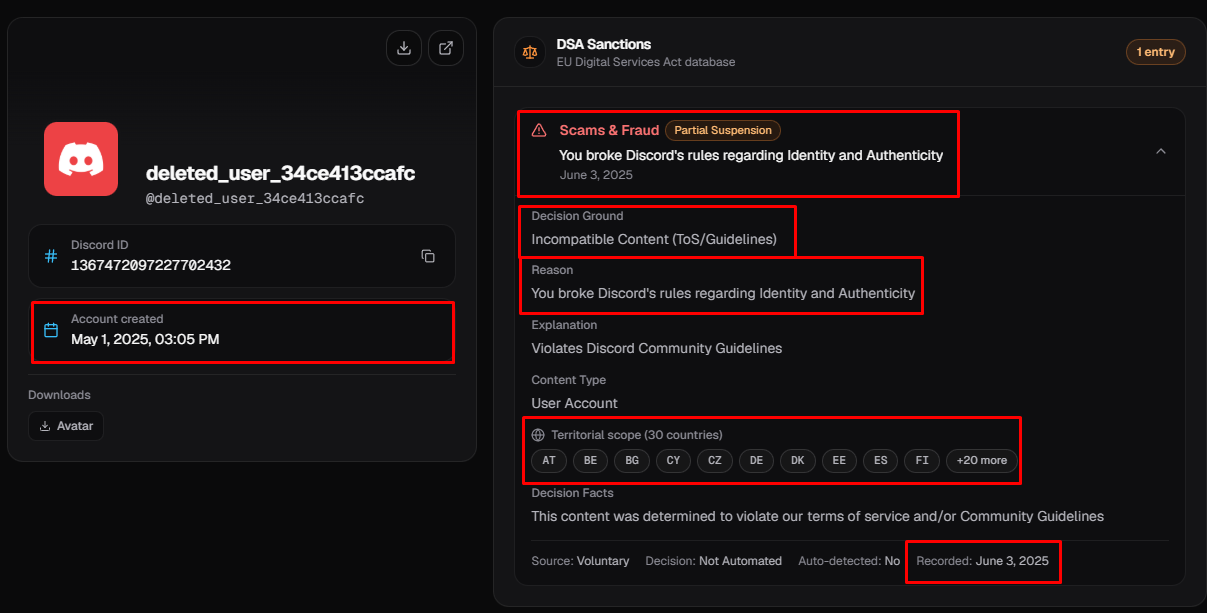
Following additional research into the account, it became evident that Discord took punitive action due to confirmed fraudulent practices, resulting in the complete deletion of both the user profile and the server. This exposes the actor’s cover story, where they deceptively attributed the takedown to simple spam issues.
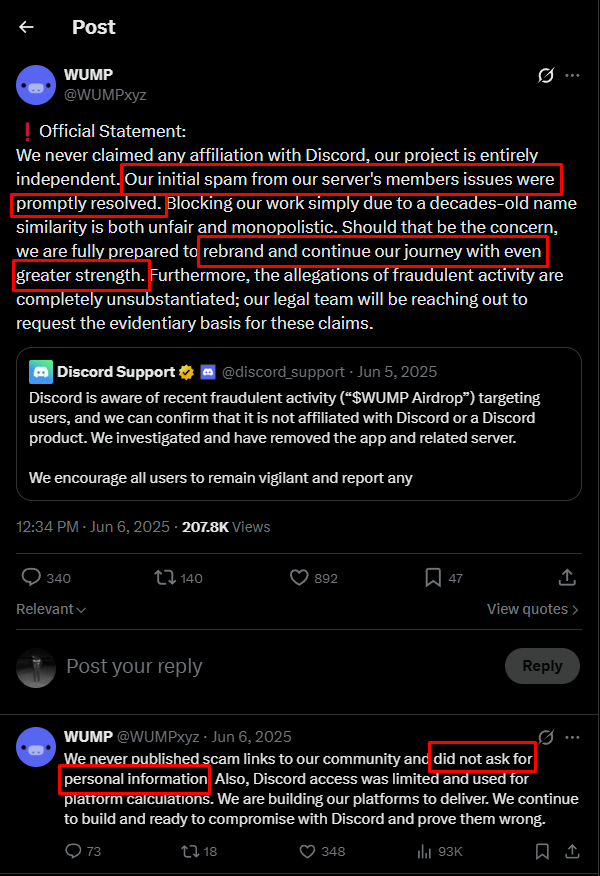
The Rebranding Narrative
In their official statements, they mentioned plans to undergo a complete rebranding and come back even stronger. Keep this detail in mind, as it will prove to be a crucial link later on.
The Telegram Community Pivot
In another reply, He mentioned that there is a telegram community for $WUMP
It was https://t.me/WUMPxyz
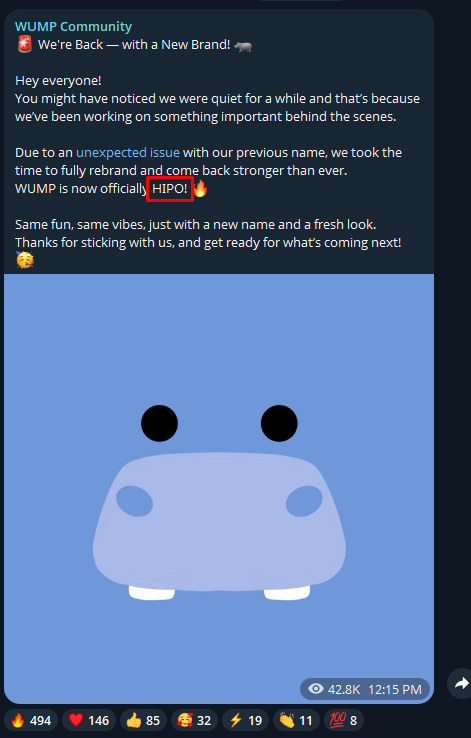
Campaign Rebirth: The Shift to $HIPO
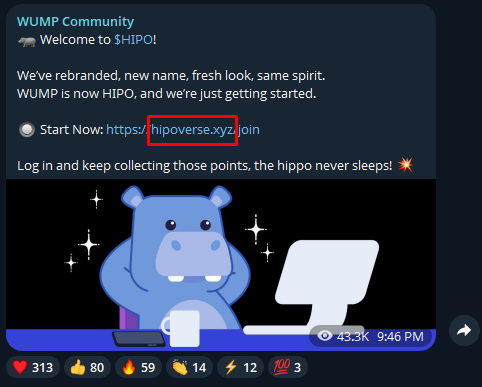
Connecting back to their promised rebranding, the very first broadcast in their newly established Telegram community confirmed the pivot: the operators had resurrected the exact same scheme under a new identity, branded as $HIPO.
New Fraudulent Infrastructure: Launch of hippoverse[.]xyz
In a follow-up message posted to the community, the cyber criminal disclosed their new landing page, revealing hippoverse[.]xyz as the active domain driving the rebranded airdrop scheme.
Passive DNS & Historical IP Analysis (Hetzner Germany)
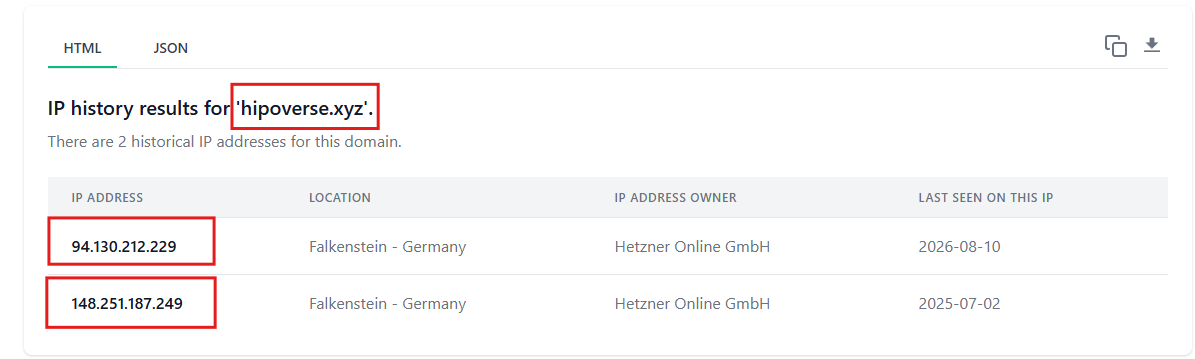
Pivoting on the target infrastructure, we performed a historical IP lookup for hipoverse.xyz to uncover backend hosting assets prior to any proxy or CDN obfuscation. The query surfaced two distinct IPv4 addresses within Hetzner Online GmbH (Falkenstein, Germany):
- 148.251.187.249, first captured during the campaign’s active period (last seen July 2, 2025).
- 94.130.212.229, identified in subsequent infrastructure updates (last seen August 10, 2026).
Reverse IP Pivoting: Mapping the Co-Hosted Assets Cluster
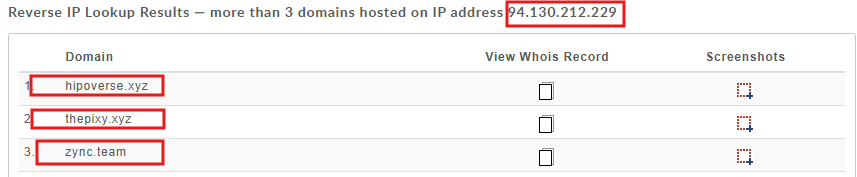
Pivoting on the latest IP address tied to the operator’s active infrastructure via reverse DNS analysis uncovered several co-hosted and historically linked hostnames. This infrastructure overlap revealed that the cyber criminal was managing multiple campaigns and assets across the same hosting environment:
hipoverse[.]xyzthepixy[.]xyzzync[.]team
WHOIS Deep-Dive: Tracking zync[.]team
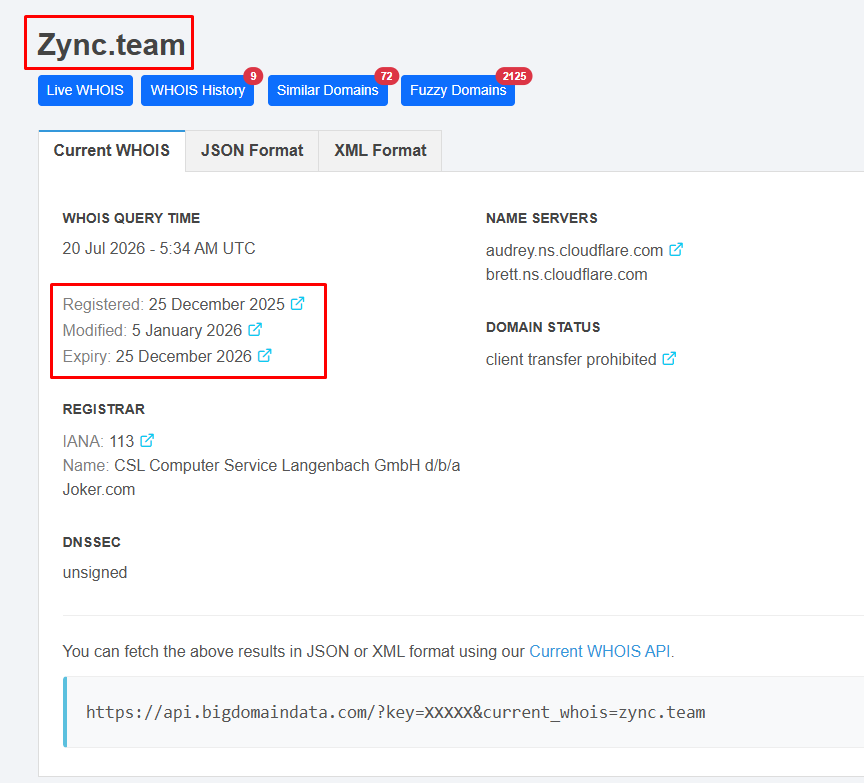
To map the cyber criminal’s subsequent infrastructure and establish operational timelines, we conducted a WHOIS query on the secondary domain Zync.team:
- Target Domain:
Zync.team - Registration Date: December 25, 2025
- Last Modified: January 5, 2026
- Expiration Date: December 25, 2026
- Registrar: CSL Computer Service Langenbach GmbH d/b/a Joker.com (IANA ID: 113)
- Name Servers:
audrey.ns.cloudflare.comandbrett.ns.cloudflare.com
The registrar data confirms the domain was registered toward the end of December 2025 via Joker.com and routed through Cloudflare’s reverse proxy infrastructure to obscure origin IP allocations. This domain serves as a key pivot point connecting re-branded assets to the original operator.
Domain Permutation Correlation: Uncovering zync[.]world
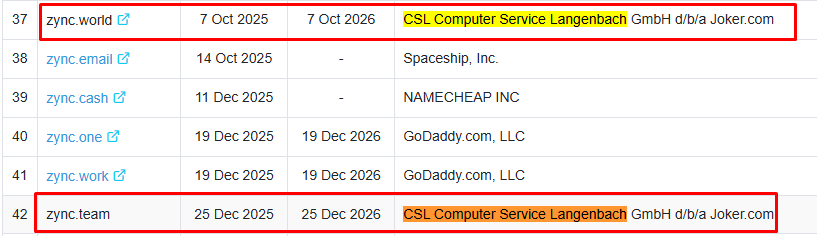
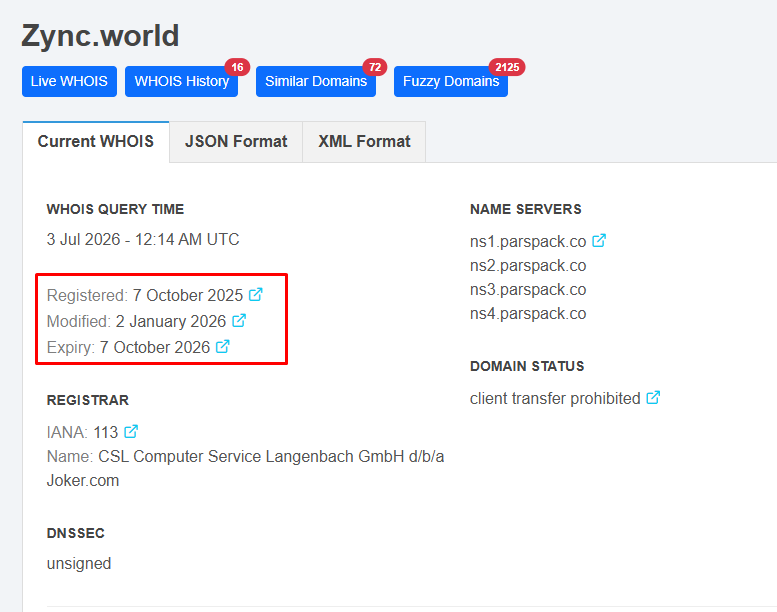
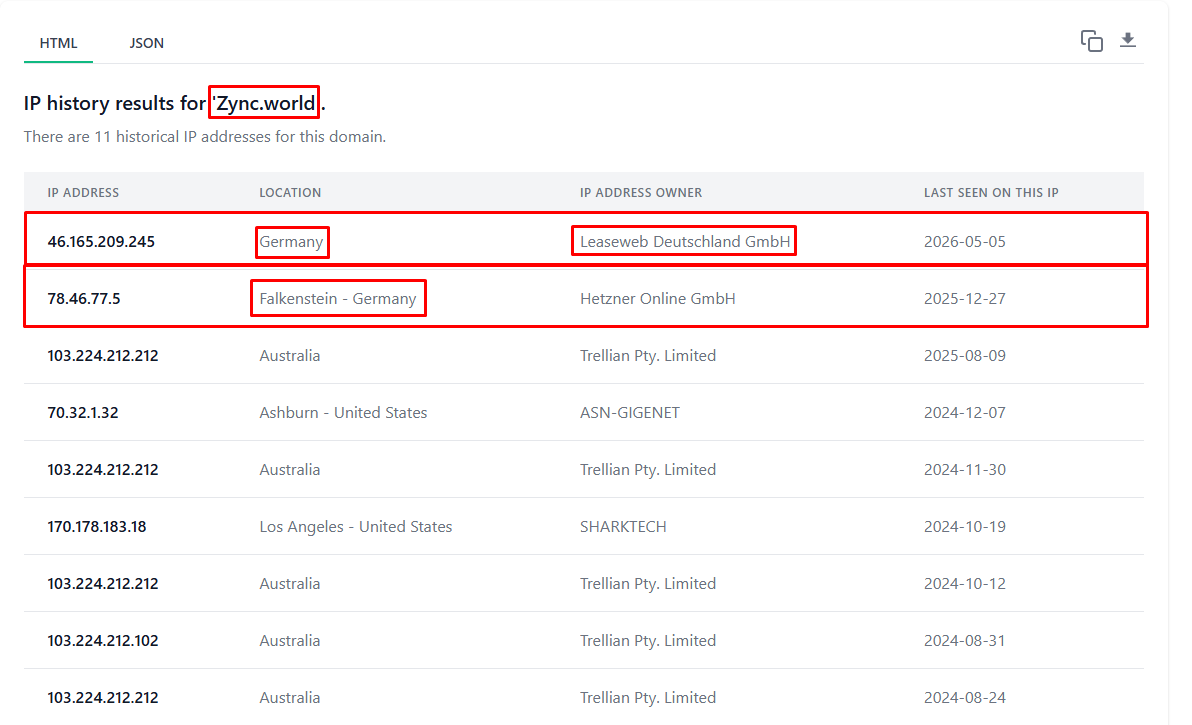
Querying for domain permutations and structurally similar naming conventions to zync[.]team surfaced zync[.]world. Cross-referencing ownership records and registration metadata confirmed that both domains belong to the exact same registrant entity, establishing a direct corporate and operational link between the two assets.
The OSINT Breakthrough: Linking to Mostafa Forouji
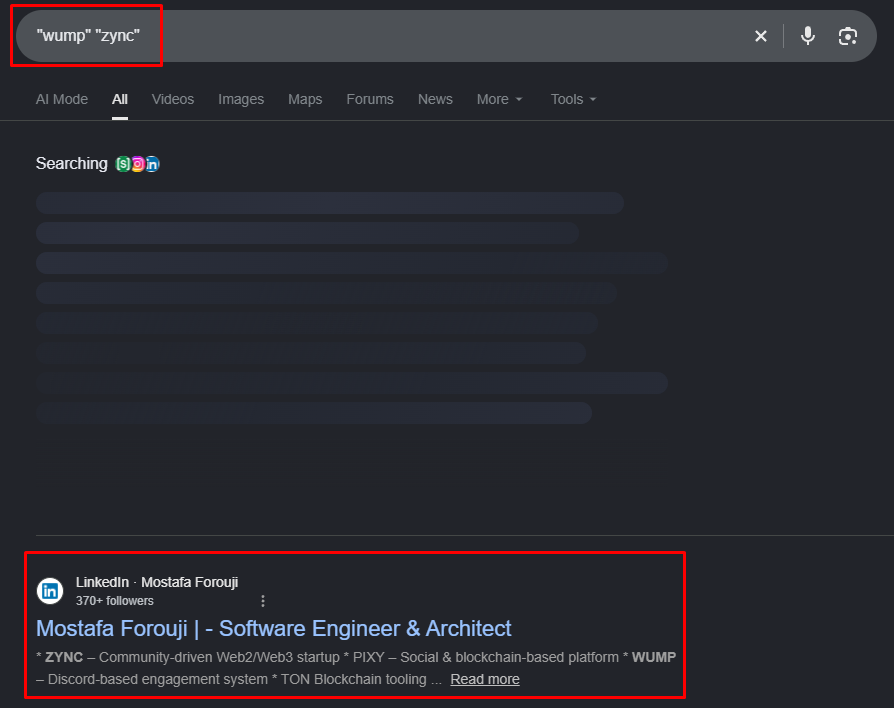
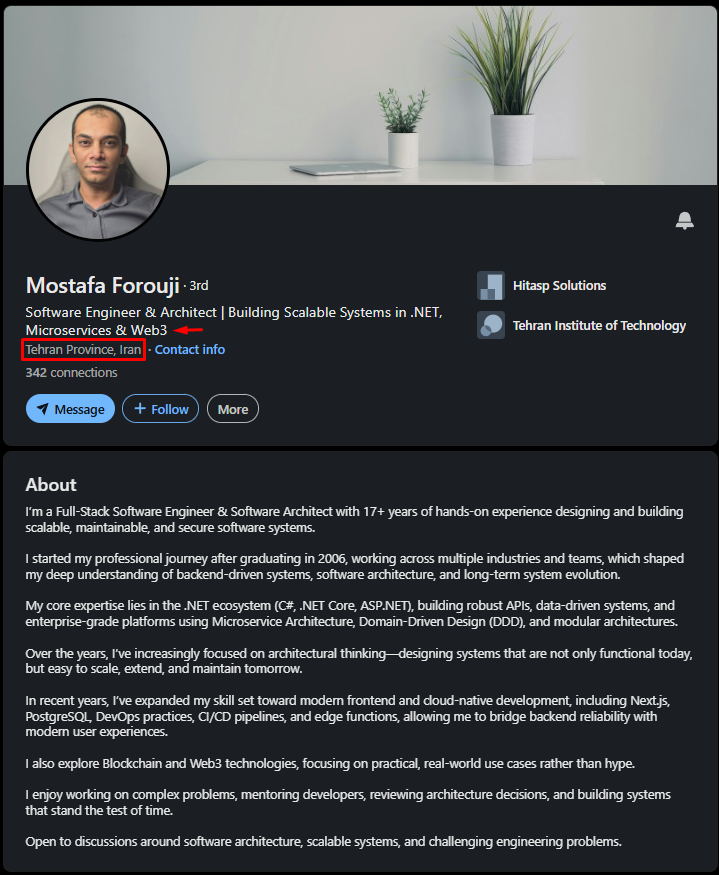
Pivoting on targeted search queries pairing "zync" with "wump" matched a specific individual profile across open sources: a LinkedIn account belonging to Mostafa Forouji. The profile aligned seamlessly with the technical markers identified throughout the preceding infrastructure analysis.
Telemetry Correlation: Iranian Origin & Web3 Skill Profile
Corroborating the OSINT findings, the profile details further solidified the attribution. The account explicitly listed the individual’s location as Iran, aligning precisely with the geographic telemetry previously leaked via an active Android session on the @WUMPxyz X/Twitter profile. Furthermore, the profile showcased a distinct background and documented technical skill set in Web3 technologies, directly corroborating the capability required to engineer decentralized application interfaces and execute crypto-themed reconnaissance campaigns.
Smoking Gun: Self-Documented Campaign History
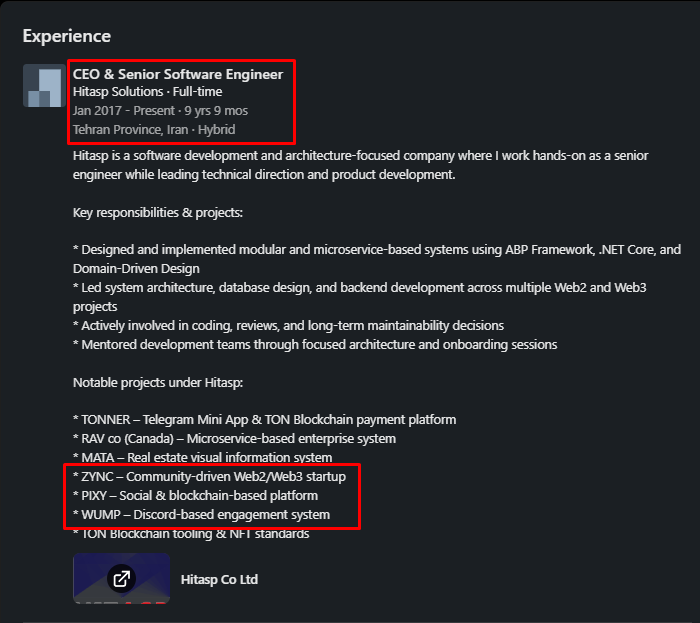
Beyond technical competencies, the individual’s profile delivered definitive attribution evidence within its documented employment history. Under the work experience section, the profile openly cataloged their active involvement in the very projects identified across our infrastructure pivots:
- ZYNC – Community-driven Web2/Web3 startup
- PIXY – Social & blockchain-based platform
- WUMP – Discord-based engagement system
This sequential timeline provides an undeniable correlation, bridging the infrastructure artifacts (zync[.]team, zync[.]world, thepixy[.]xyz, and the $WUMP campaign) directly to a single operational actor.
Non-Repudiation: Corporate Mentions & Direct Attribution
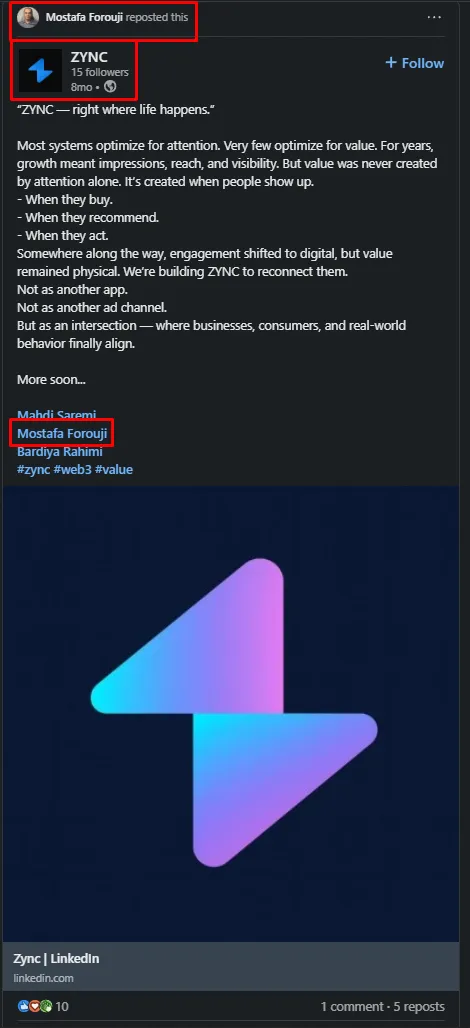
Corroborating the profile claims, behavioral activity on the account provided additional non-repudiation evidence. The subject had reposted content published directly by the ZYNC company page, wherein the original post explicitly tagged and mentioned the individual as an active member of their core operational team.
Corporate Identity Convergence: The zync[.]world Anchor
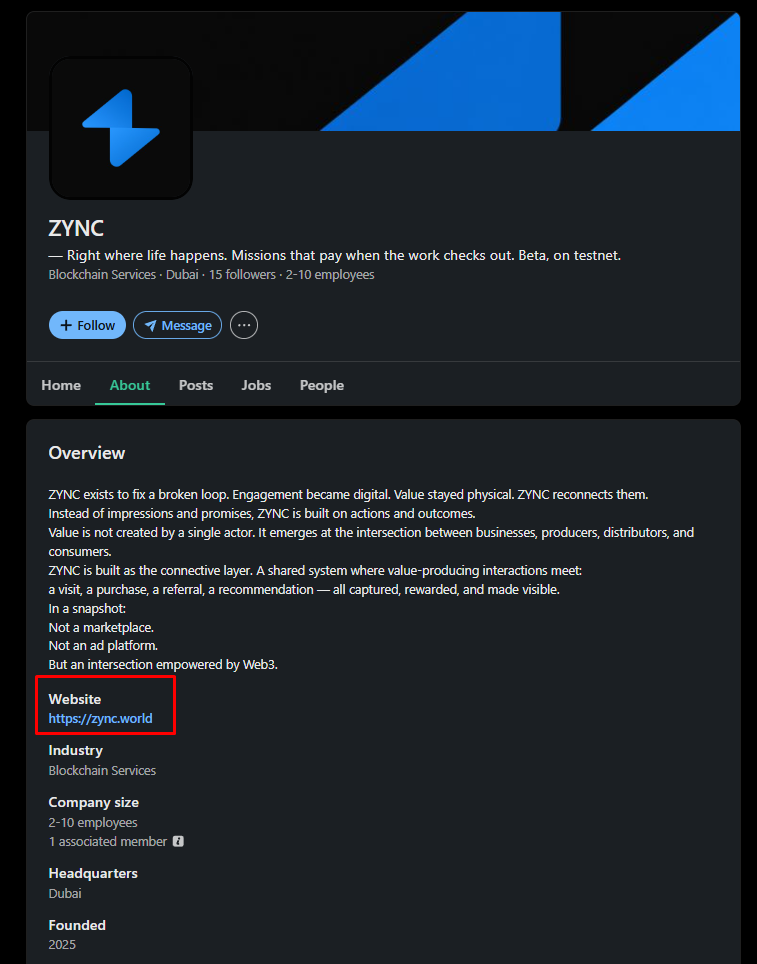
The company’s public metadata provided the final connective link. In the “About” overview of the ZYNC page, the referenced website was none other than zync[.]world—the exact permutation discovered earlier alongside zync[.]team. This corroboration definitively ties the physical entity, the corporate entity, and the malicious campaign infrastructure together.
Complete Physical Attribution: Portfolio & Social Footprint Exposure
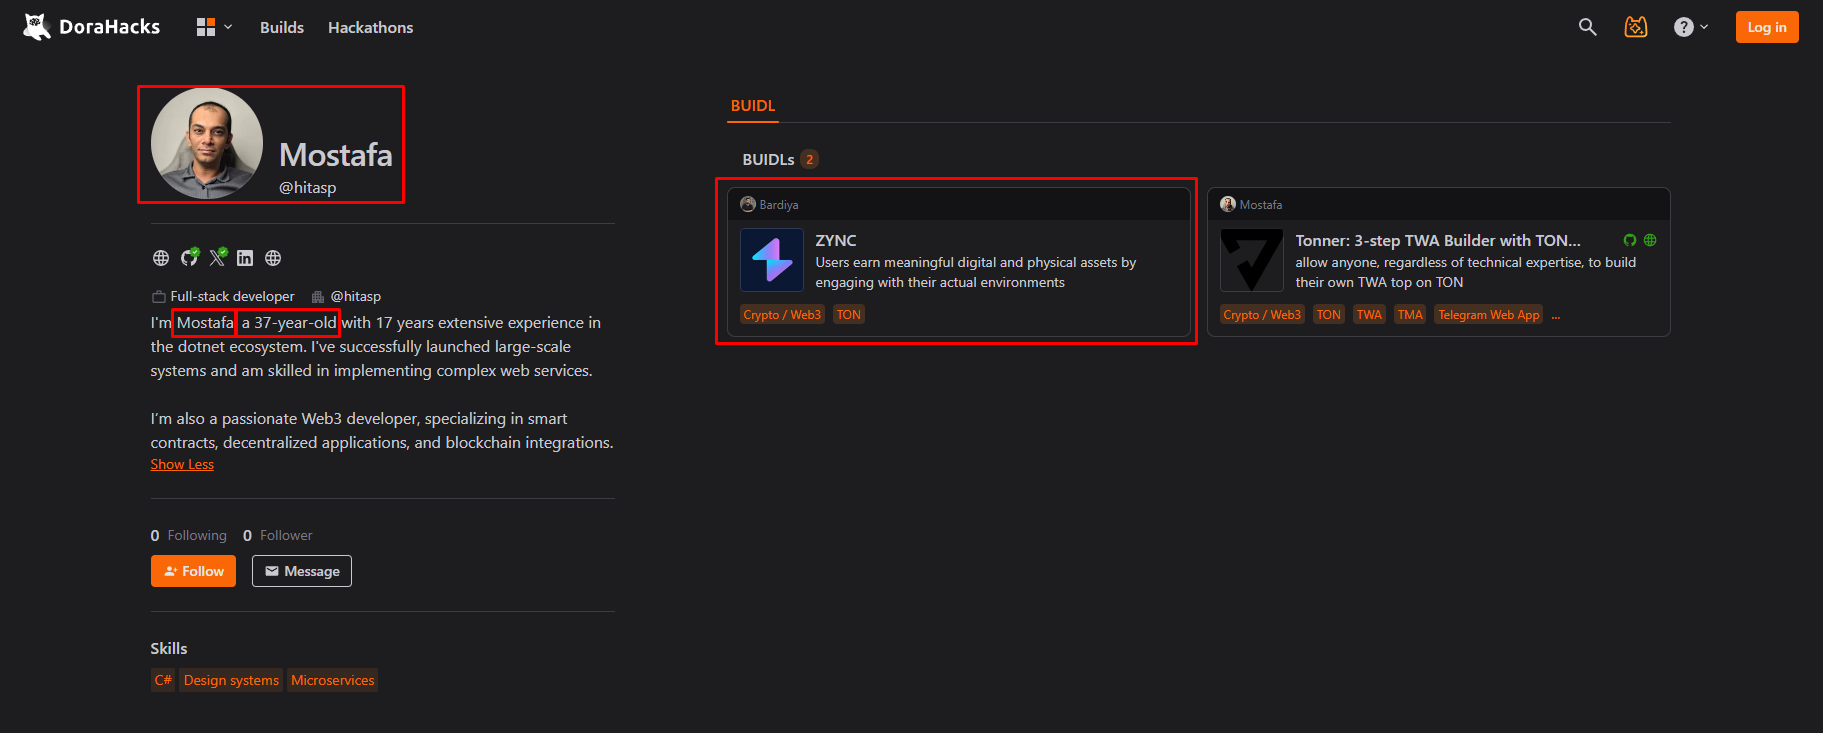
Pivoting further through Google dorks revealed an active personal portfolio belonging to the cyber actor. The discovered page contained comprehensive identifying artifacts: a verified photograph, his full name, an age of 37, direct references to his work with ZYNC, and direct outbound links to his various social media channels, decisively anchoring the entire operational infrastructure to a single, unmasked physical individual.
Conclusion & Key Takeaways
The investigation into the fraudulent Web3 campaigns across $WUMP,$HIPO, and ZYNC highlights how catastrophic OPSEC failures can completely unravel an actor’s anonymity. What began as a deceptive airdrop operation collapsed due to a chain of unforced operational errors:
- Geographic Leaks: Attempted to spoof a German location, but leaked real Android connections originating from Iran.
- Recurrent German Spoofing: Germany was repeatedly leveraged as a false operational front; the actor consistently routed hosting infrastructure through German servers locations to project European legitimacy and mask real-world origins in Iran.
- Archived Metadata: Expired Discord invites permanently exposed the threat actor’s immutable User ID (
1367472097227702432) and handle (itsleooo). - Infrastructure Re-use: Reverse IP pivots showed the operator co-hosted multiple scam domains—
hipoverse[.]xyz,thepixy[.]xyz, andzync[.]team—on the exact same server. - Public Self-Attribution: The actor documented these exact projects (WUMP, PIXY, ZYNC) on his public LinkedIn profile, while official company posts tagged him directly.
- Full De-anonymization: Google dorking exposed a personal portfolio revealing his full identity: Mostafa Forouji, age 37, based in Iran, complete with facial photos and personal social accounts.
- Operational Outlook: While individual domains and Discord servers were taken down for fraud, the operator consistently recycles the exact same infrastructure and playbook under new tickers. High-confidence attribution firmly anchors the entire network to Mostafa Forouji.