
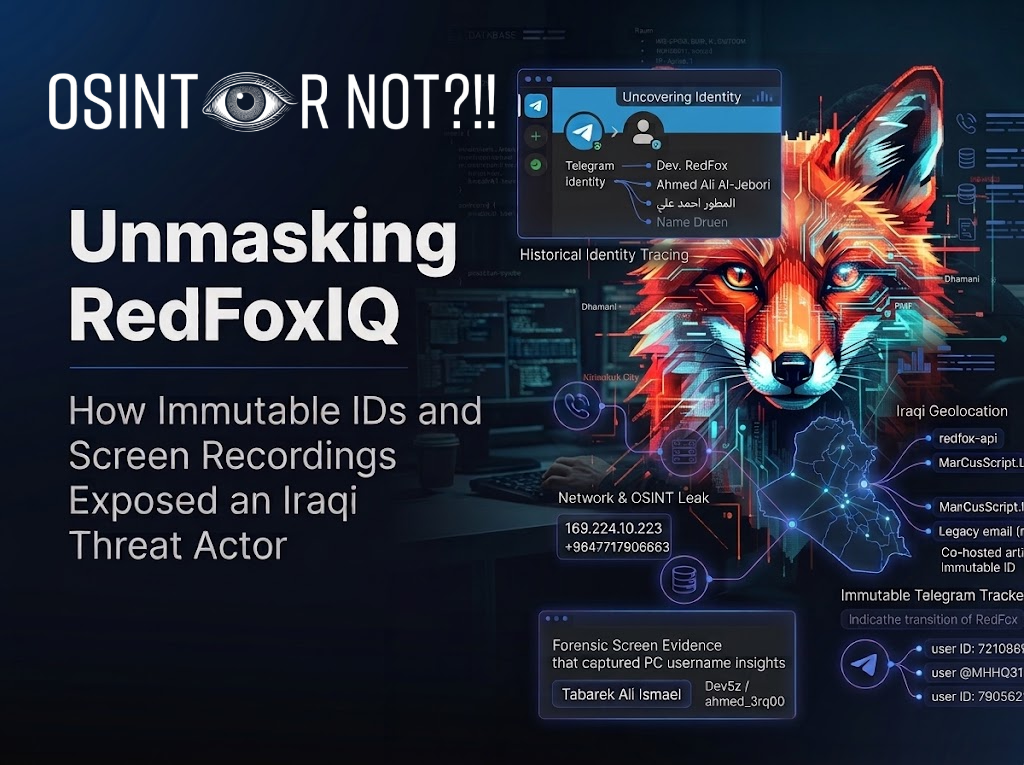
Who Is RedFoxIQ ?
RedFoxIQ (also known by aliases RedFox7z and Dev2z and RedFox6z and Dev5z and RedFox Cyber ) is an independent, active cyber threat actor specializing in web intrusion, database exfiltration, and unauthorized access exposure.
Originating from Iraq, this threat actor operates a highly active digital footprint, targeting vulnerable web infrastructure to extract and expose sensitive information. The use of a rotating network of aliases indicates a deliberate operational security (OpSec) strategy designed to fragment his digital trail, evade attribution, and complicate tracking.
Compromise Timeline and Targets
| Date | Target / Entity | Compromise Details | Source |
|---|---|---|---|
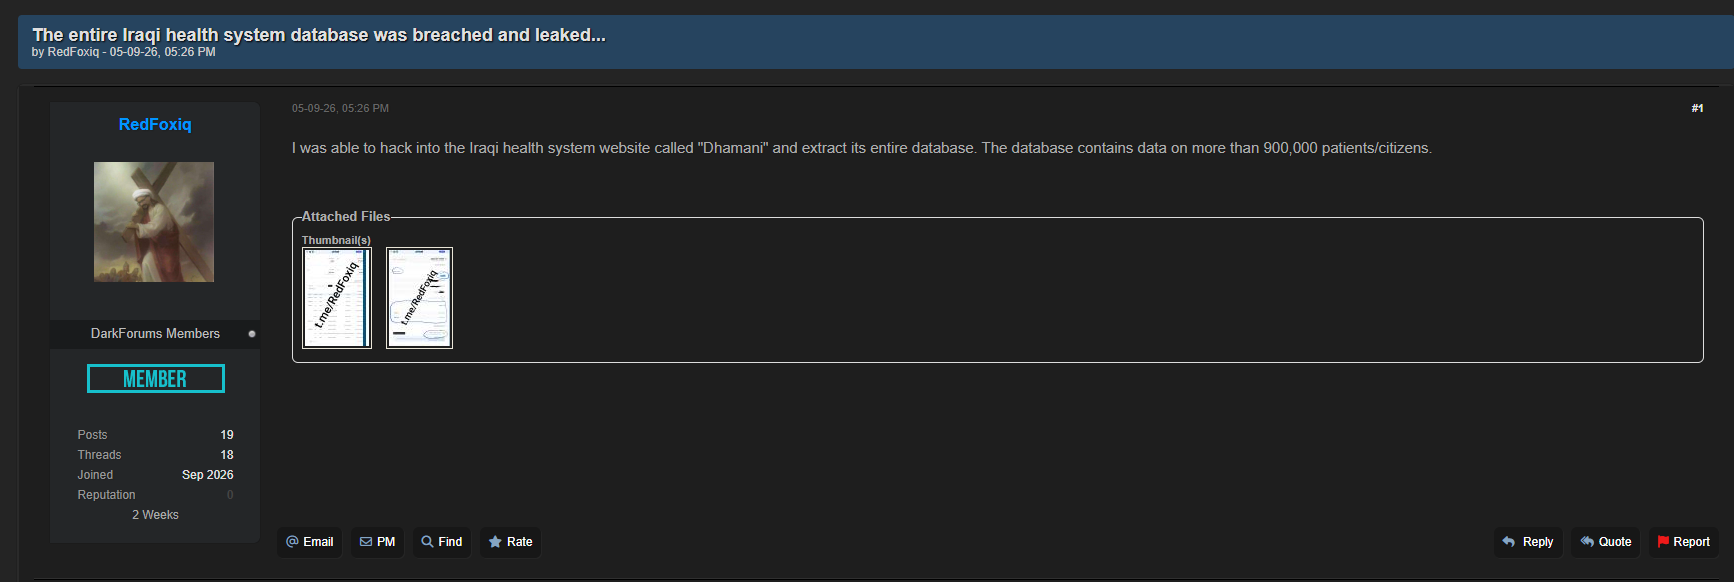
| September 5, 2026 | Iraqi health system (“Dhamani”) | Claimed extraction of the entire database containing data on more than 900,000 patients/citizens. | Forums |
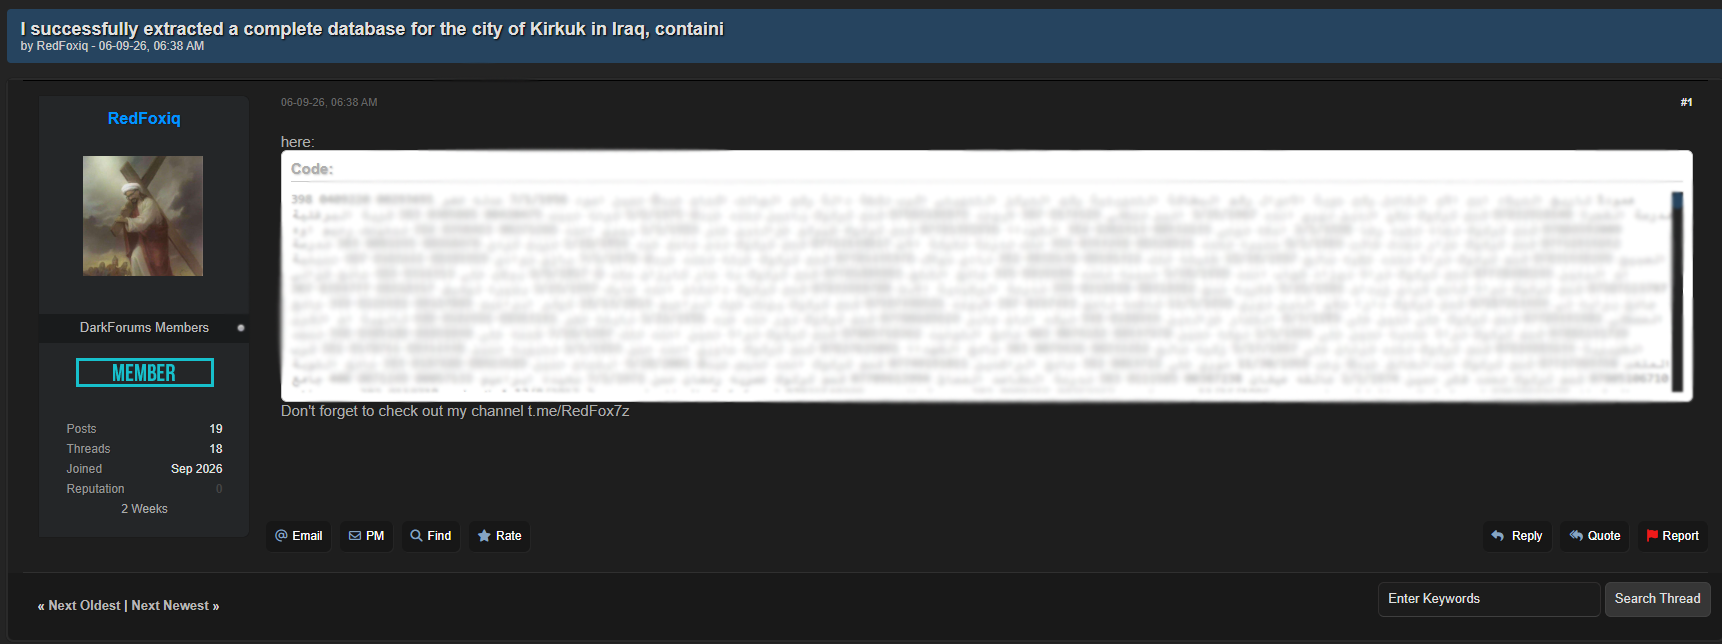
| September 6, 2026 | Kirkuk City Database (Iraq) | Claimed extraction of a complete citizen database containing names, dates of birth, mothers’ names, identity numbers, ration-card data, and phone numbers. | Forums |
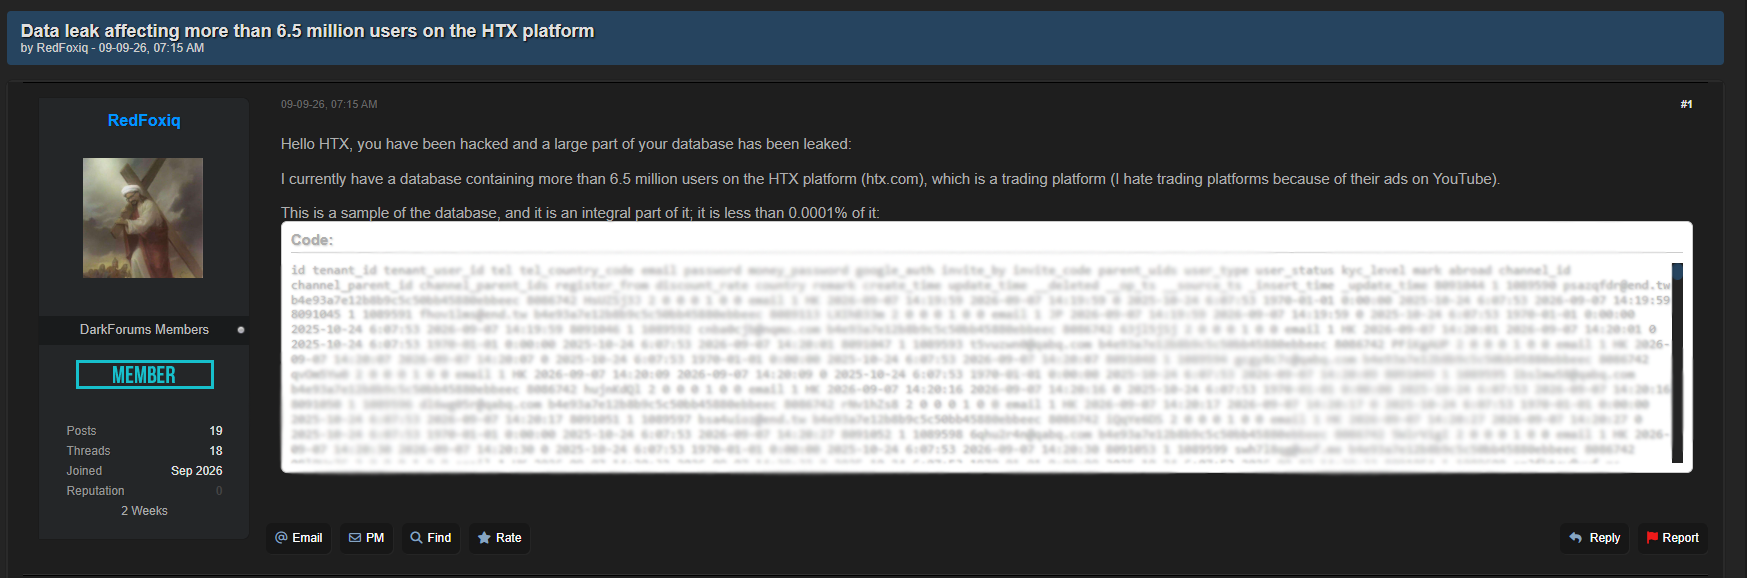
| September 7, 2026 | HTX (Breach Date) | Alleged compromise of >6.5 million user records, including emails, phone numbers, passwords, and KYC data. | Forums |
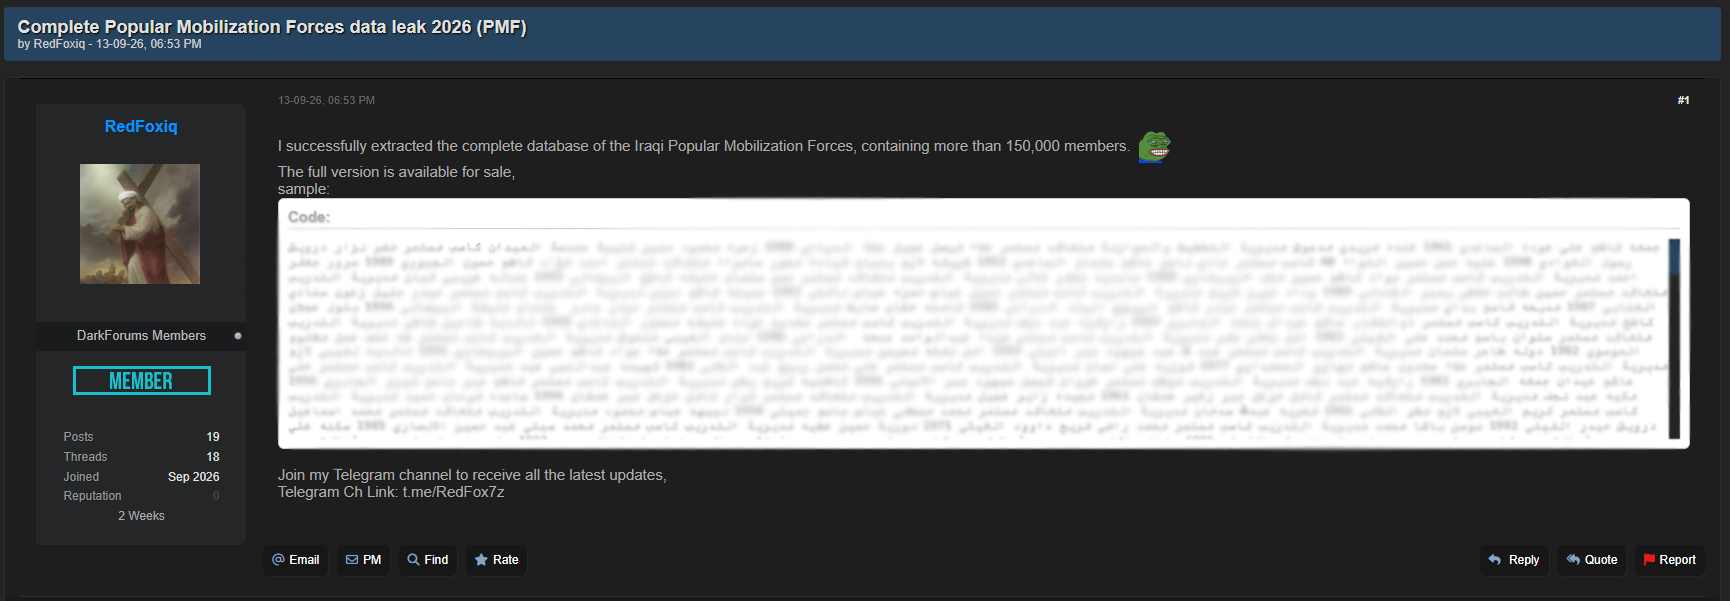
| September 13, 2026 | Popular Mobilization Forces - PMF (Iraq) | Claimed a database of >150,000 members. Posted samples with full names, birth years, family details, and assigned units, offering the file for sale. | Forums |
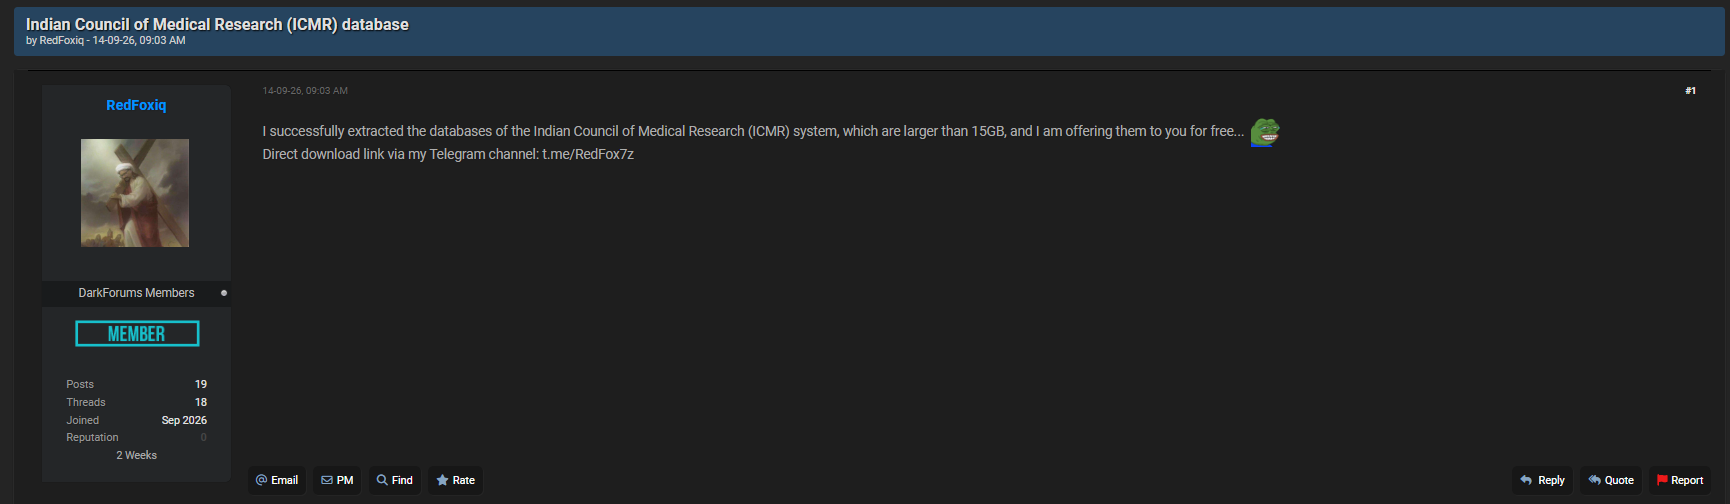
| September 14, 2026 | Indian Council of Medical Research - ICMR (India) | Claimed extraction of >15GB of records, stating intent to release the data for free on Telegram. | Forums |
| September 15, 2026 | Bangladesh Fisheries Authority | Claimed compromise of >8,000 fishermen records, exposing names, registration IDs, villages, dates of birth, and approval status. | Forums |
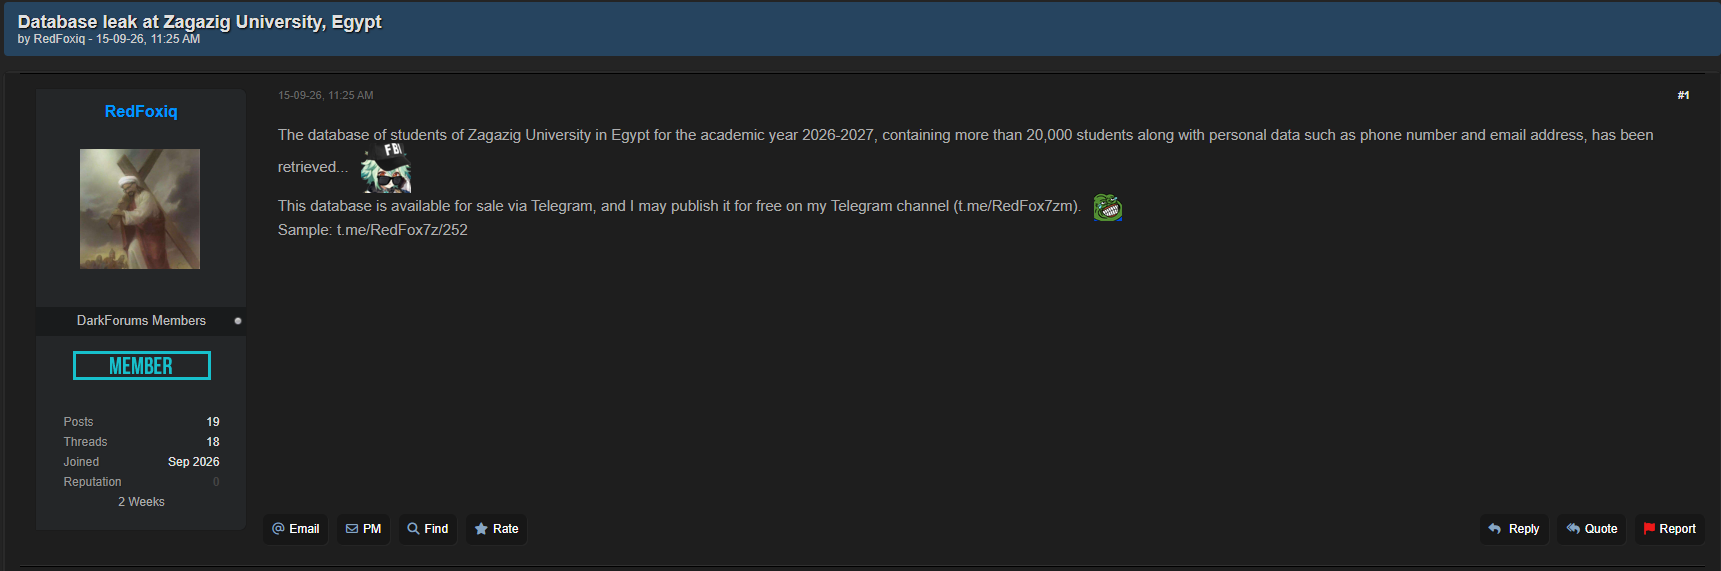
| September 15, 2026 | Zagazig University (Egypt) | Claimed database of >20,000 students (2026–2027 academic year) including personal details, phone numbers, and emails, with threats to sell or dump. | Forums |
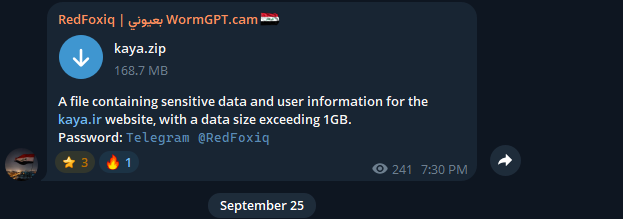
| September 24, 2026 | kaya.ir (Iran) | Announced publication of >1GB of data via alias @RedFox7z and uploaded a 168.7MB file (kaya.zip) locked with a password tied to @RedFoxiq. |
Telegram |
| September 29, 2026 | The Financial Regulatory Authority - FRA (Egypt) | Claimed extraction of >15GB of sensitive data, distributed across 4 files containing records spanning from 2022 to 2026. | Telegram |
GitHub Account Discovery
Searching for the RedFox7z alias revealed an associated GitHub account.
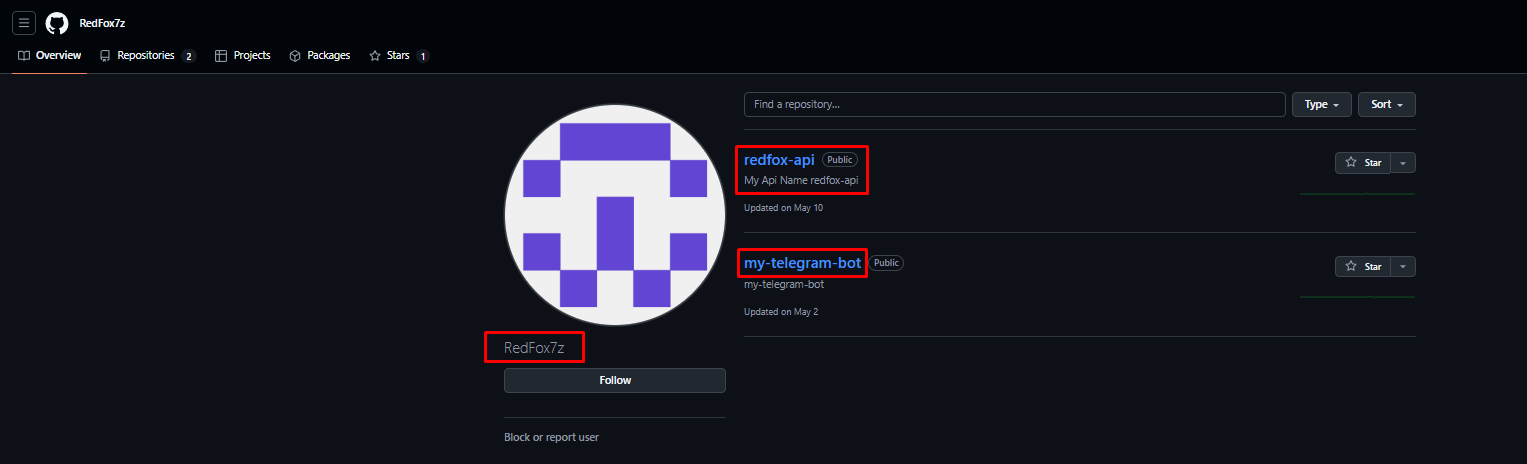
The account features two public repositories:
redfox-api: Described as “My Api Name redfox-api”, last updated on May 10.my-telegram-bot: Described as “my-telegram-bot”, last updated on May 2.
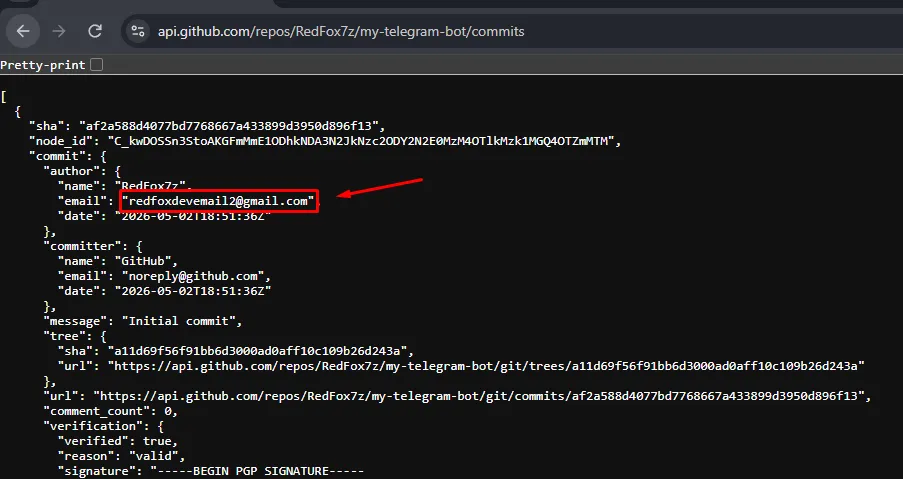
Upon reviewing the my-telegram-bot repository, the developer’s email address was identified within the commit metadata.
- Email:
[email protected]
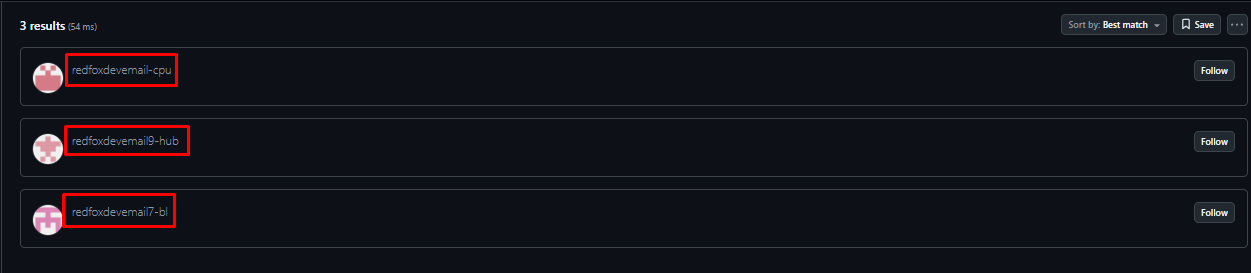
A brief search revealed that the alias extracted from the leaked email address had previously been used to register older accounts on GitHub.
Github Accounts :
- redfoxdevemail-cpu
- redfoxdevemail9-hub
- redfoxdevemail7-cpu
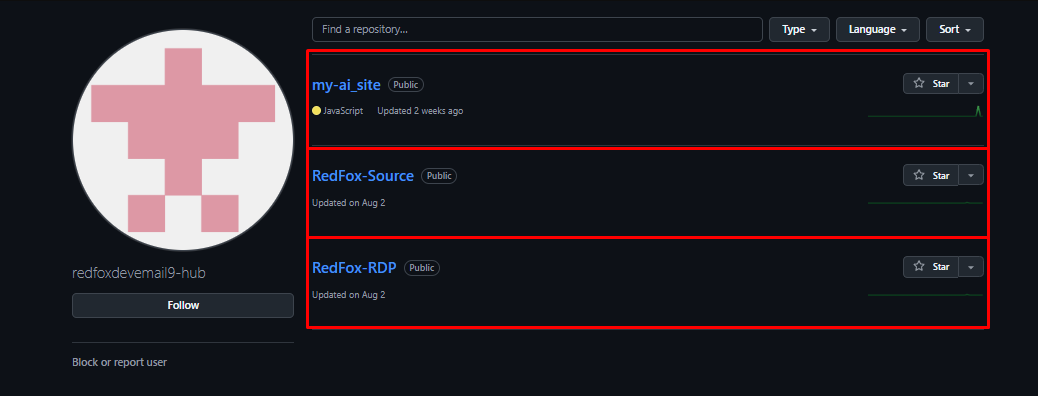
Upon examining the redfoxdevemail9-hub account , we found that it contains 3 public repositories.
my-ai_site: last updated 2 weeks agoRedFox-Source: last updated on Aug 2RedFox-RDP: last updated on Aug 2
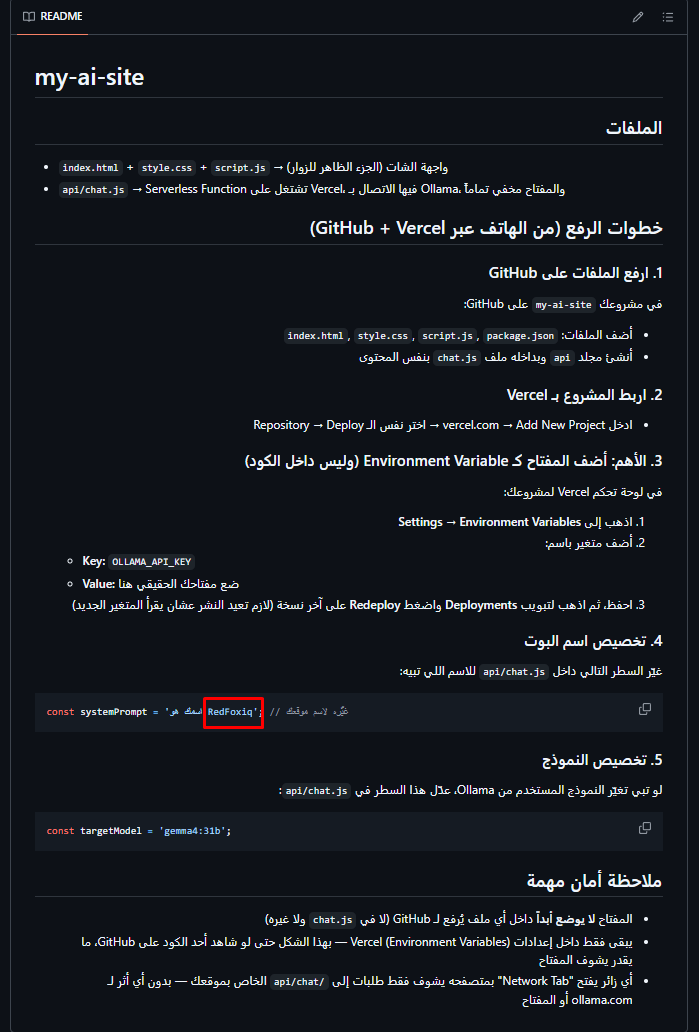
Further analysis of the repositories revealed a critical piece of evidence: the threat actor explicitly mentioned his primary black hat username as an example within a README file. This crucial oversight serves as direct confirmation tying these developer accounts to his malicious online identity.
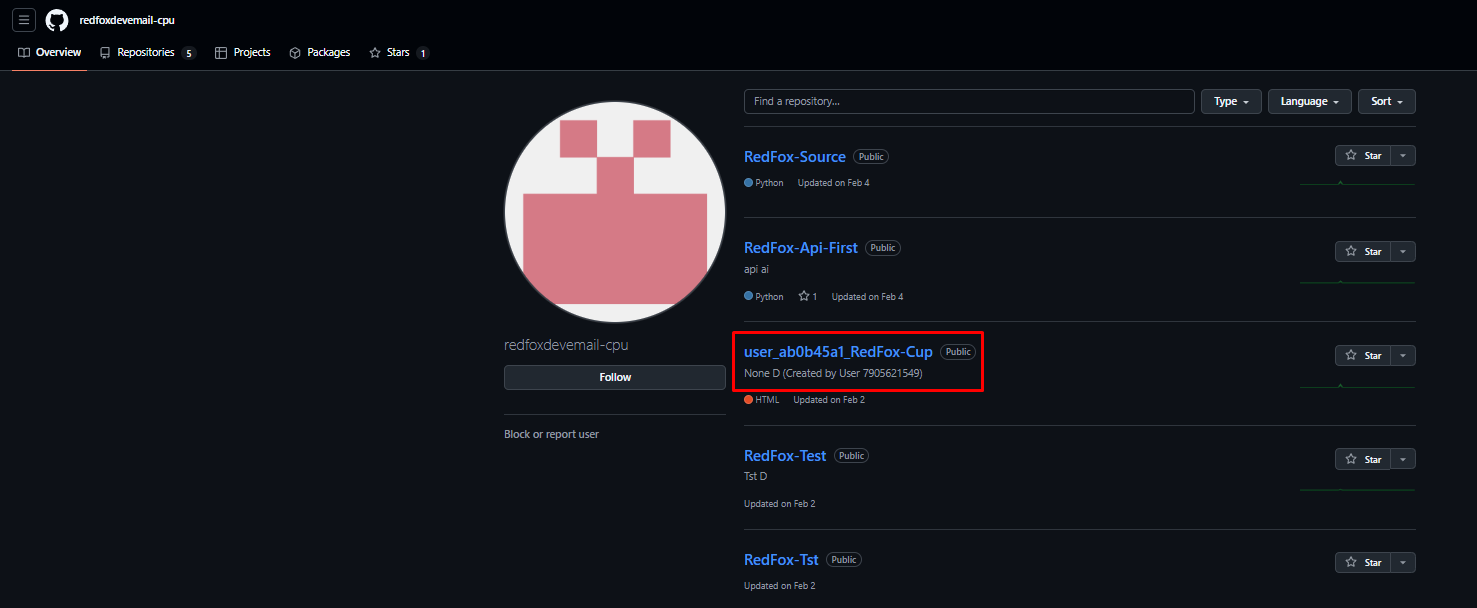
Upon examining the redfoxdevemail-cpu account too , we found that it contains 5 public repositories.
A critical discovery within this account is the user_ab0b45a1_RedFox-Cup repository. Its description explicitly states “(Created by User 7905621549)”, exposing the threat actor’s old Telegram User ID. This provides a direct, verifiable link tying this GitHub profile back to his previous Telegram operations.
Telegram ID Tracking and Historical Aliases
We used the actor’s Telegram User ID to dig deeper into his history. Since this ID cannot be changed, we tracked it to find their past digital footprint. We discovered that the actor changed their identity several times using these old names:
| Date | Display Name (First / Last Name) |
|---|---|
| 2026-05-10 | RedFox² |
| 2026-05-10 | R℮dFox |
| 2026-04-13 | M |
| 2026-04-13 | M💗 |
| 2026-03-12 | 𝗥𝗲𝗱𝗙𝗼𝘅 |
| 2026-03-07 | 𝗥𝗲𝗱𝗙𝗼𝘅 |
| 2026-03-03 | RedFox (معتزل فترة) |
| 2026-02-24 | RedFox (ماسح تلجرام) |
| 2026-02-13 | R℮dFox ² |
| 2026-02-06 | RedFox ² 卍 |
| 2026-01-15 | RedFox*2 |
Video Tutorials and Screen Recording Leaks
By tracking his activity across different Telegram groups, we discovered a crucial message. The actor shared a link to his personal channel, which he used for posting tutorials.
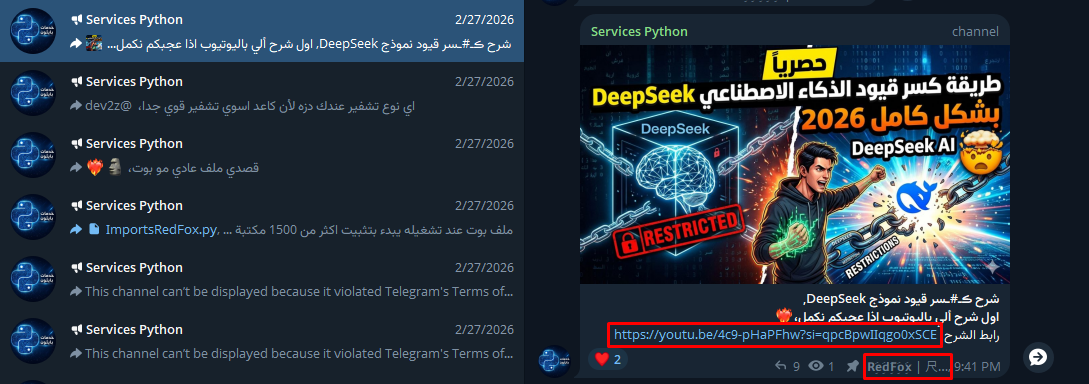
The video clearly displays the name ‘RedFox Cyber’, the associated username ‘’@Dev2z’', and his previous logo.
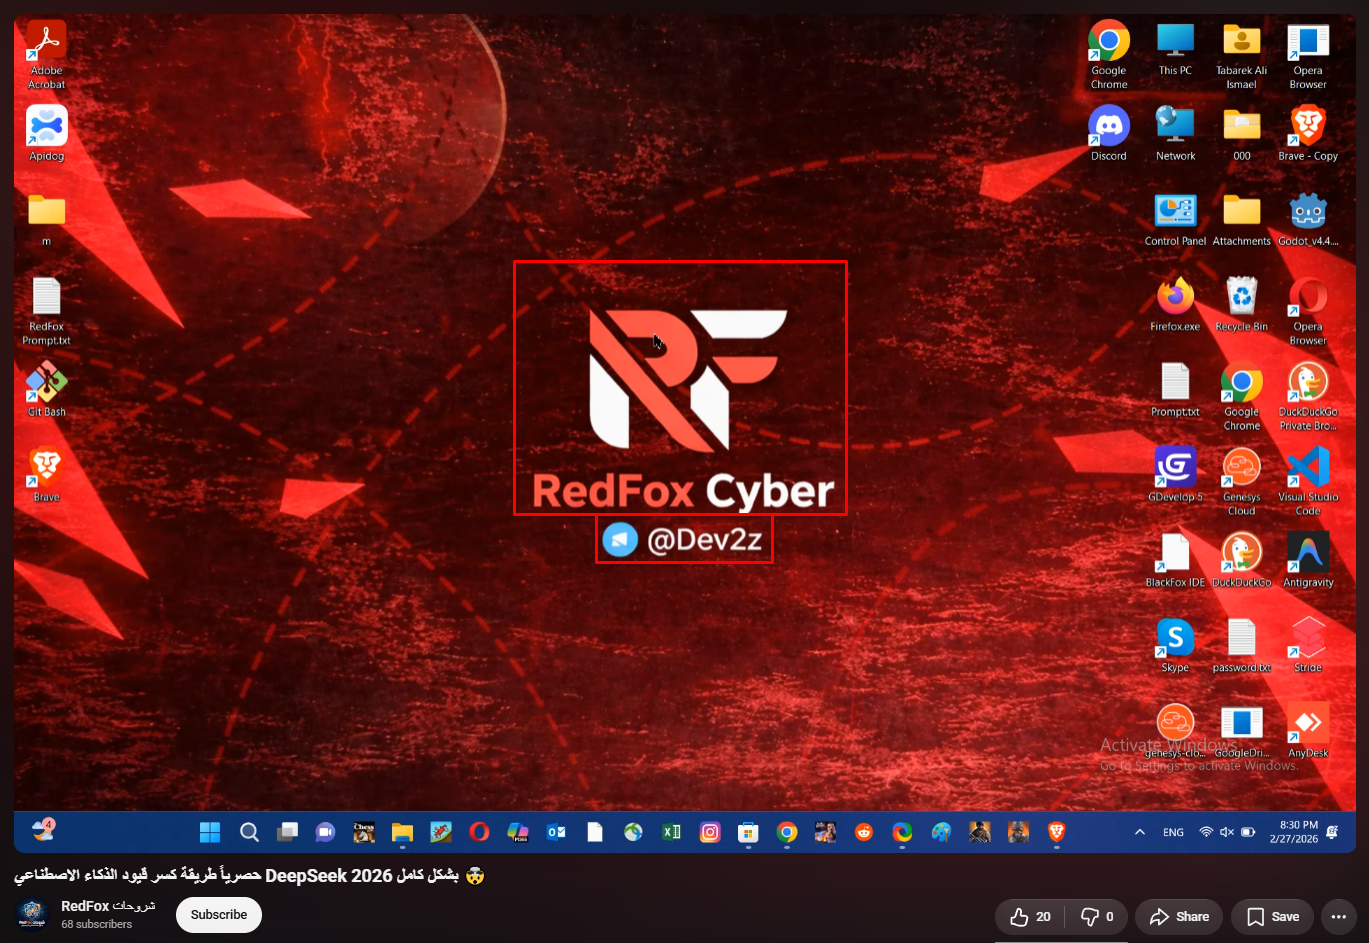
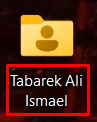
During the first few seconds of the video, we noticed the computer’s username is set to ‘Tabarek Ali Ismael’. This is a major clue that points directly to someone close to him.
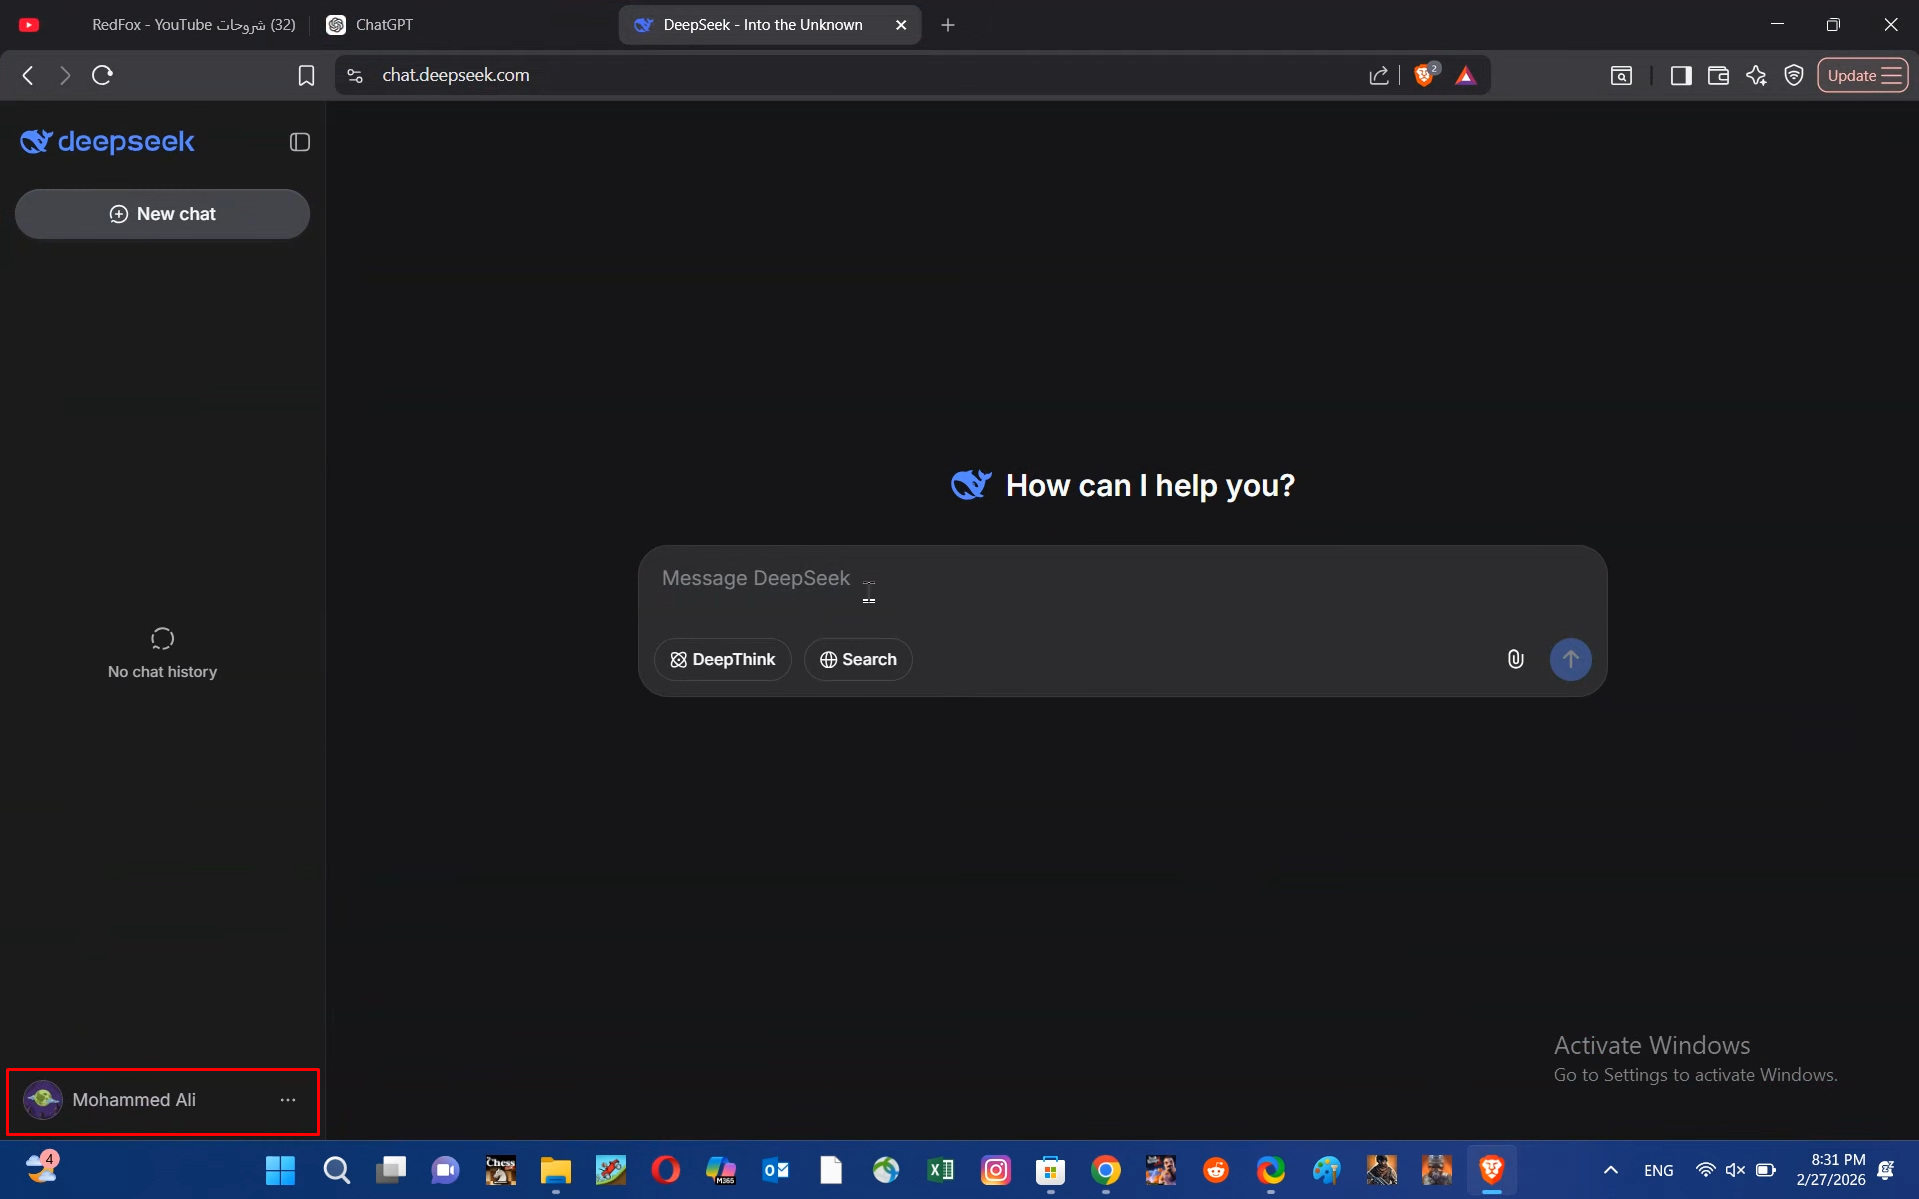
At exactly 0:19 in the video, the name ‘Mohammed Ali’ appears. This means the threat actor or his brother might be named Mohammed, and it implies their father’s name is Ali.
Gaming Profiles and YouTube Footprint
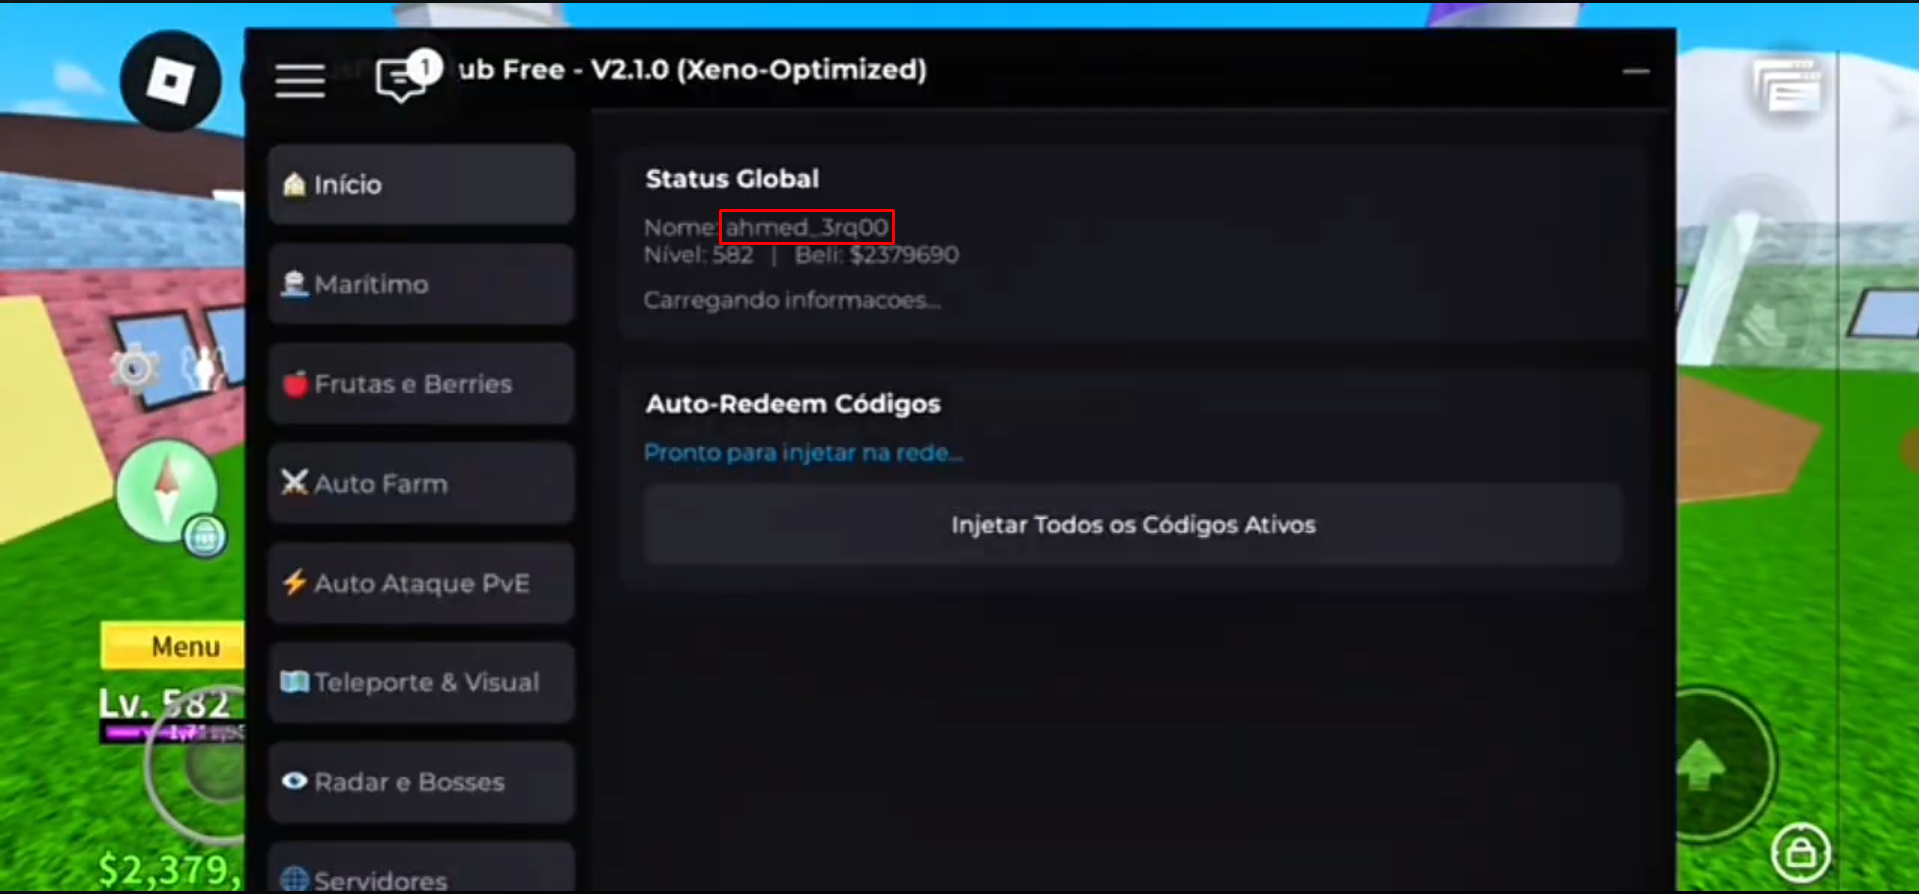
Another intriguing finding was a second video related to Roblox, which showed the threat actor actively playing the game.
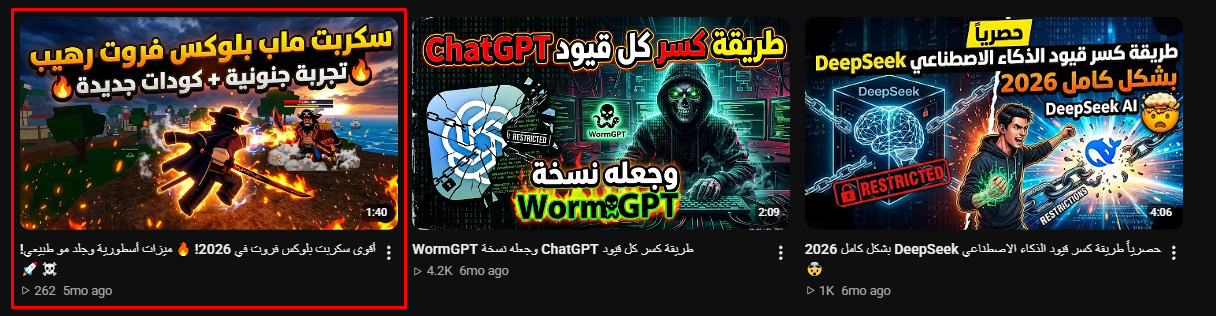
At 0:17 in the video, we noticed his Roblox username was ‘ahmed_3rq00’ .
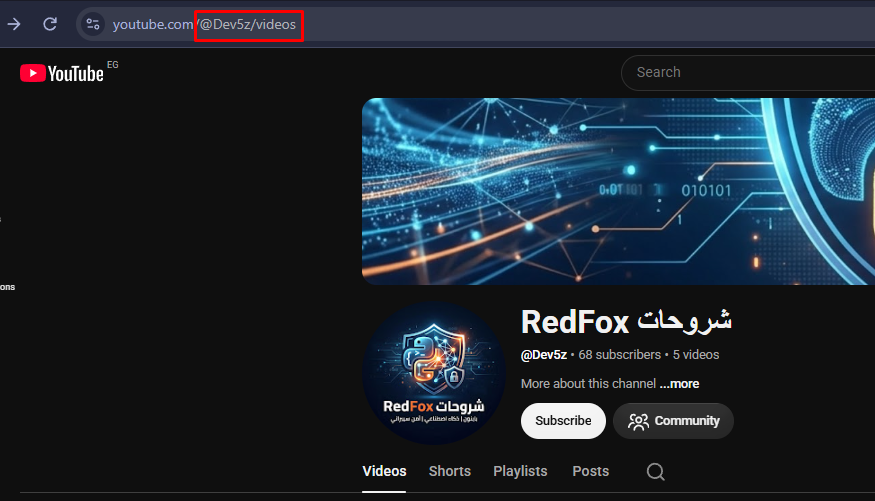
Analysis of the YouTube channel revealed an interesting username used as the account handle: ‘Dev5z’.
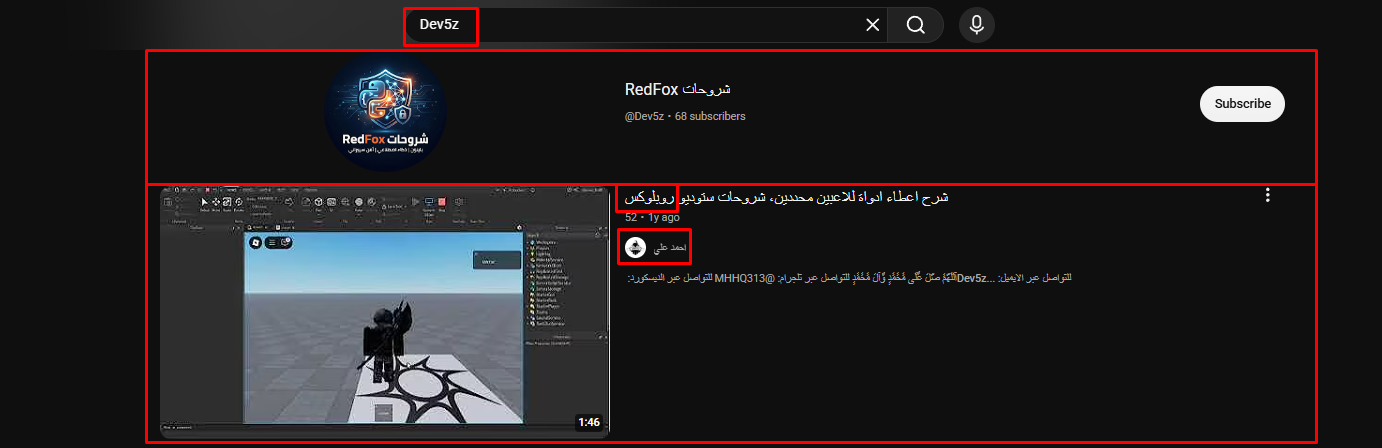
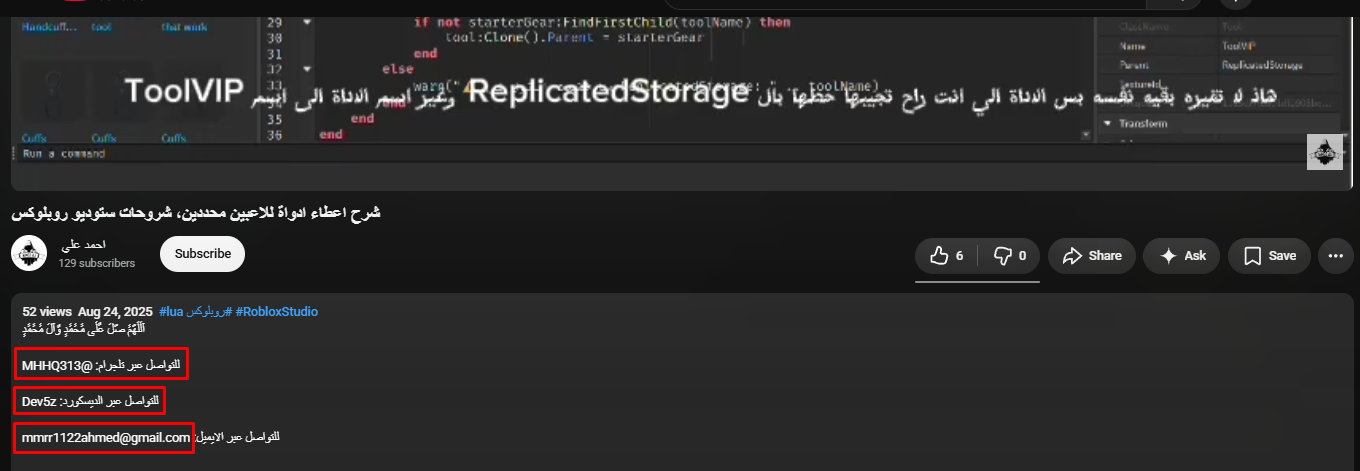
After searching for this username on YouTube, we found a Roblox tutorial video made by someone named ‘Ahmed Ali’.
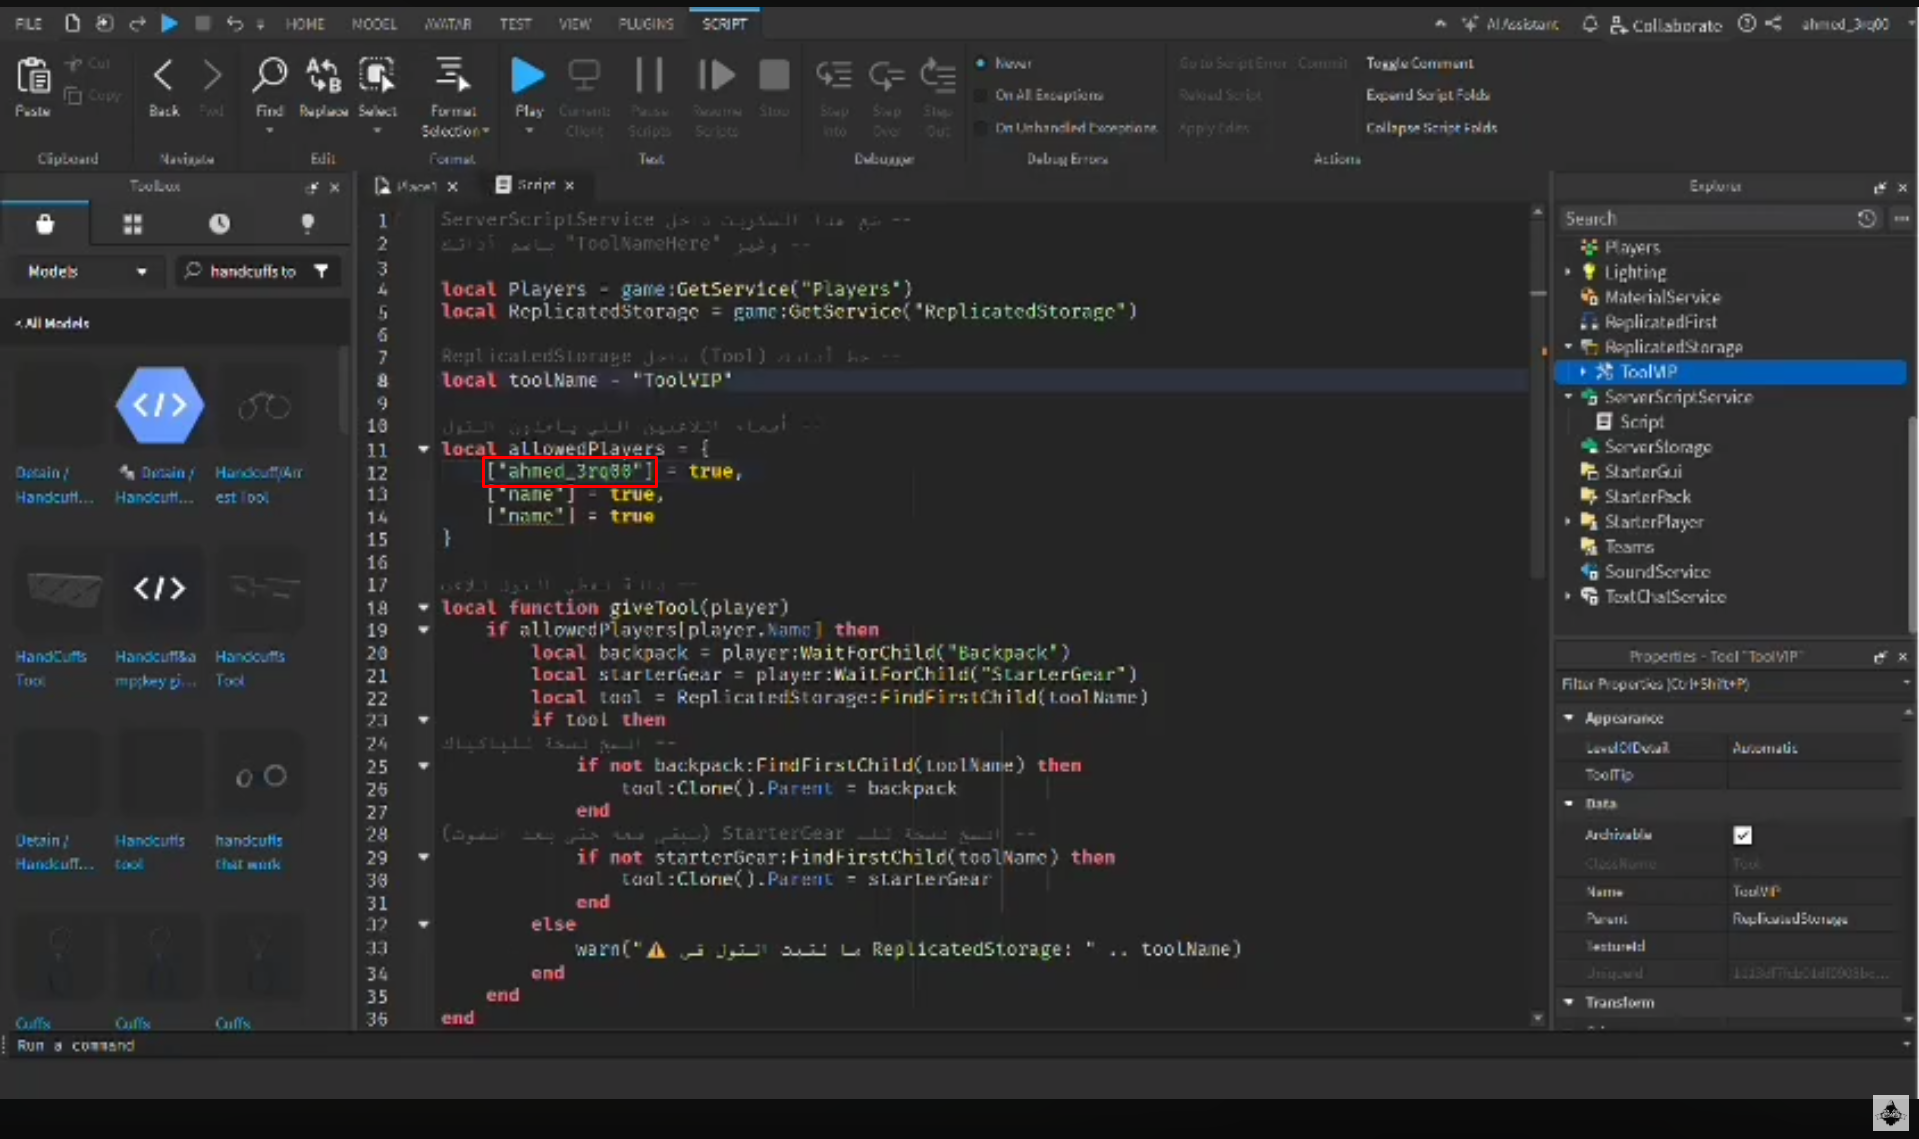
At 0:39 in the video, the username ‘ahmed_3rq00’ is clearly visible. This correlates directly with the username identified on the previous channel, confirming that this is the same threat actor.
A review of the video’s description exposed further contact details and identifiers, explicitly listing :
- Email Address:
[email protected] - Older Telegram Account: ‘
@MHHQ313’ - Discord Username:
Dev5z(matching the previously discovered handle).
Email Analysis and Connected Platforms
After conducting a thorough analysis of the email address [email protected], we successfully uncovered three additional accounts linked to the threat actor. Interestingly, these accounts confirm his past and his strong connection to the programming and development field:
- An account on the Adalo platform under the name ‘ahmed ali’.
- An account on Duolingo where he explicitly named himself ‘المطور احمد علي’ (Developer Ahmed Ali).
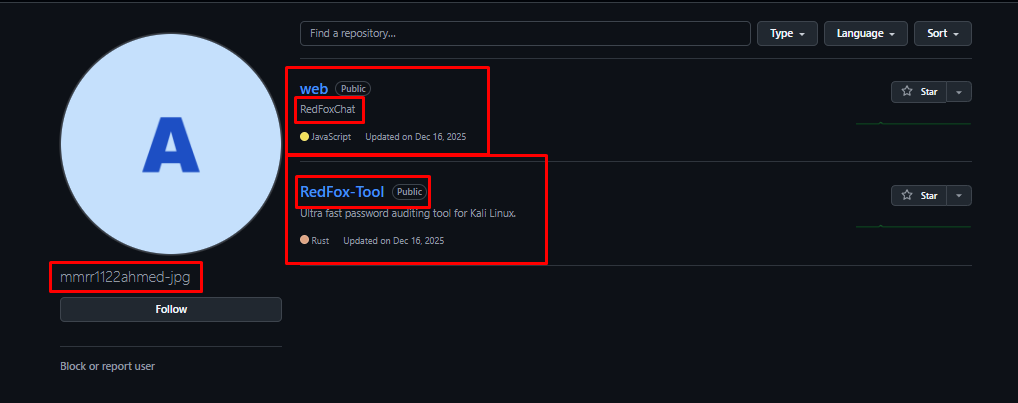
- An account on GitHub, a platform dedicated to developers under the username ‘mmrr1122ahmed-jpg’
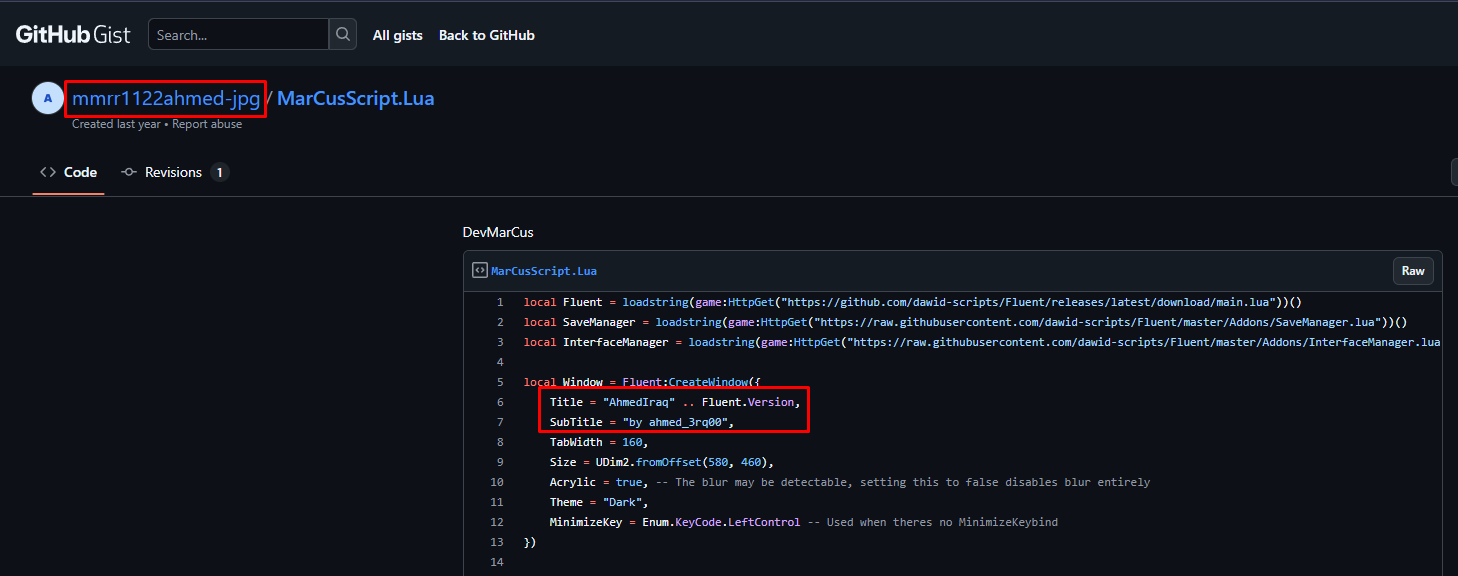
In one of his GitHub Gists, we found a file named MarCusScript.Lua. Inside it, the text showed ‘AhmedIraqi’ and ‘by ahmed_3rq00’, which exactly matches the Roblox username we discovered earlier
Discord Verification and Historical Telegram Timeline
When we investigated the Discord username further, we discovered that the account’s display name was set to ‘RedFox’, bringing us back to his primary alias.
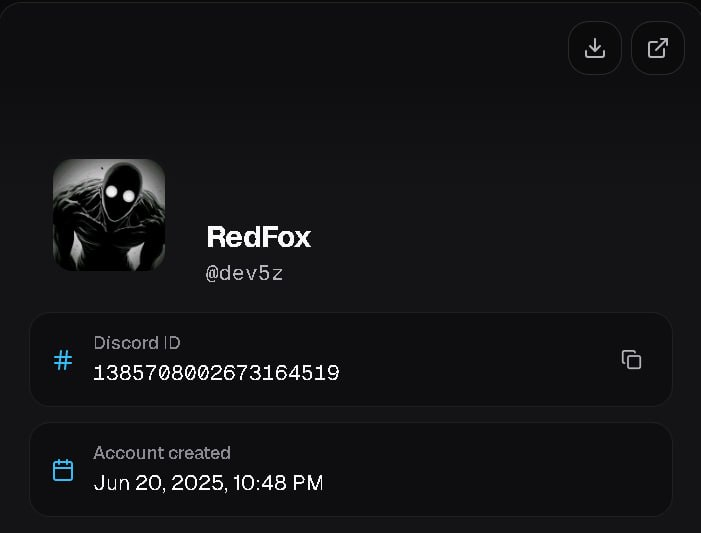
By further analyzing the older Telegram username, @MHHQ313 we extracted a comprehensive historical log of the display names registered to this account over time. This timeline not only tracks his online presence back to 2024 but also repeatedly confirms his real name and his developer persona: @MHHQ313
| Date | Display Name (First / Last Name) |
|---|---|
| 2026-03-16 | Dev. RedFox |
| 2026-03-16 | Аhm℮d Ali |
| 2025-11-10 | المطور احمد علي |
| 2025-06-25 | احمد علي |
| 2025-06-07 | الكاتب احمد علي |
| 2025-05-29 | 𝗮𝗵𝗺𝗲𝗱 𝗮𝗹-𝗷𝗲𝗯𝗼𝗿𝗶 - غير متصل |
| 2025-05-28 | 𝗮𝗵𝗺𝗲𝗱 𝗮𝗹-𝗷𝗲𝗯𝗼𝗿𝗶 - معتزل امتحانات |
| 2025-05-04 | 𝗮𝗵𝗺𝗲𝗱 𝗮𝗹-𝗷𝗲𝗯𝗼𝗿𝗶 - مـمـول |
| 2025-04-20 | 𝗮𝗵𝗺𝗲𝗱 𝗮𝗹-𝗷𝗲𝗯𝗼𝗿𝗶 |
| 2025-04-11 | αh𝗆𝖾ძ α𝗅Ꭵ |
| 2025-03-27 | معتزل αh𝗆𝖾ძ α𝗅Ꭵ |
| 2025-03-25 | كاعد اقره αh𝗆𝖾ძ α𝗅Ꭵ |
| 2025-03-11 | احمد علي معتزل |
| 2025-03-09 | احمد عليᴹ |
| 2025-03-07 | احمد علي • ثالث ا • |
| 2025-02-27 | احمد علي • ثالث ا • ᴮ¹⁰ |
| 2025-02-16 | احمد علي • معتزل فترة |
| 2025-02-01 | 💤 احمد علي 💤 |
| 2025-01-31 | احمد علي • نايم |
| 2025-01-28 | احمد علي نايم |
| 2025-01-04 | احمد علي • ثالث ا • معتزل • |
| 2024-11-11 | معتزل (دراسة) |
| 2024-10-20 | 1* Ahmed |
| 2024-10-09 | 🖤 |
Database Leaks and Final De-anonymization
To solidify our findings, we cross-referenced his data with known Telegram databases and leaks. This led to a critical discovery: we found his leaked phone number. Notably, out of all his deleted accounts, this was the only Iraqi (+964) number, further confirming his geographic location. The leaked record contained the following details :
- Phone Number:
+9647717906663 - Telegram ID:
7210869087 - Username:
@MHHQ313 - Note: The only IQ number found across all his deleted accounts
Conclusion & Key Takeaways
The investigation into the threat actor RedFoxIQ highlights how catastrophic OPSEC failures and digital footprint fragmentation can completely unravel a cybercriminal’s anonymity. What began as a sophisticated campaign of database exfiltration targeting high-profile entities across the Middle East and Asia collapsed due to a chain of unforced operational errors:
- Metadata & Version Control Leaks: The actor failed to sanitize GitHub environments, exposing developer emails (
[email protected]) in commit metadata. He also explicitly documented his black-hat persona in public README files and hardcoded his immutable Telegram User ID (7905621549) directly into a repository description. - Screen Recording Oversights: Self-published video tutorials inadvertently captured his local computing environment, exposing real-name machine users (‘Tabarek Ali Ismael’ and ‘Mohammed Ali’) and linking family connections directly to his operational workstation.
- Cross-Platform Handle Re-use: The operator consistently recycled specific aliases—such as
Dev5zandahmed_3rq00—across Discord, YouTube, Roblox, and Telegram, allowing investigators to bridge his malicious infrastructure to his personal gaming and developer profiles. - Immutable Identifier Tracking: By pivoting on static Telegram User IDs, historical data tracking defeated his strategy of rotating display names. The alias timeline exposed his real name and documented his transition from a student (“معتزل امتحانات” / “احمد علي”) to his current threat actor persona.
- Self-Attribution via Developer Accounts: A leaked video description exposed his personal email (
[email protected]), which was directly registered to platforms like Adalo, GitHub, and Duolingo under his explicit real name, “المطور احمد علي” (Developer Ahmed Ali). - Full De-anonymization: Cross-referencing his legacy Telegram handle (
@MHHQ313) with known database leaks yielded the final, definitive link: an Iraqi phone number (+9647717906663). Combined with his historical display names (“ahmed al-jebori”) and script artifacts (“AhmedIraqi”), the threat actor is firmly identified as Ahmed Ali Ismael Al-jebori, based in Iraq. - Operational Outlook: While RedFoxIQ attempts to mask his tracks with a vast network of rotating aliases (RedFox7z, Dev2z, etc.), his foundational operational security is deeply flawed. He continuously reuses the same email structures, static IDs, and developer habits. High-confidence attribution firmly anchors this entire cybercrime network to Ahmed Ali Ismael Al-jebori.